
Your security partner, powered by AI, operated by humans
Round-the-clock protection that blends analyst expertise with purpose-built AI to stop threats before they become breaches.
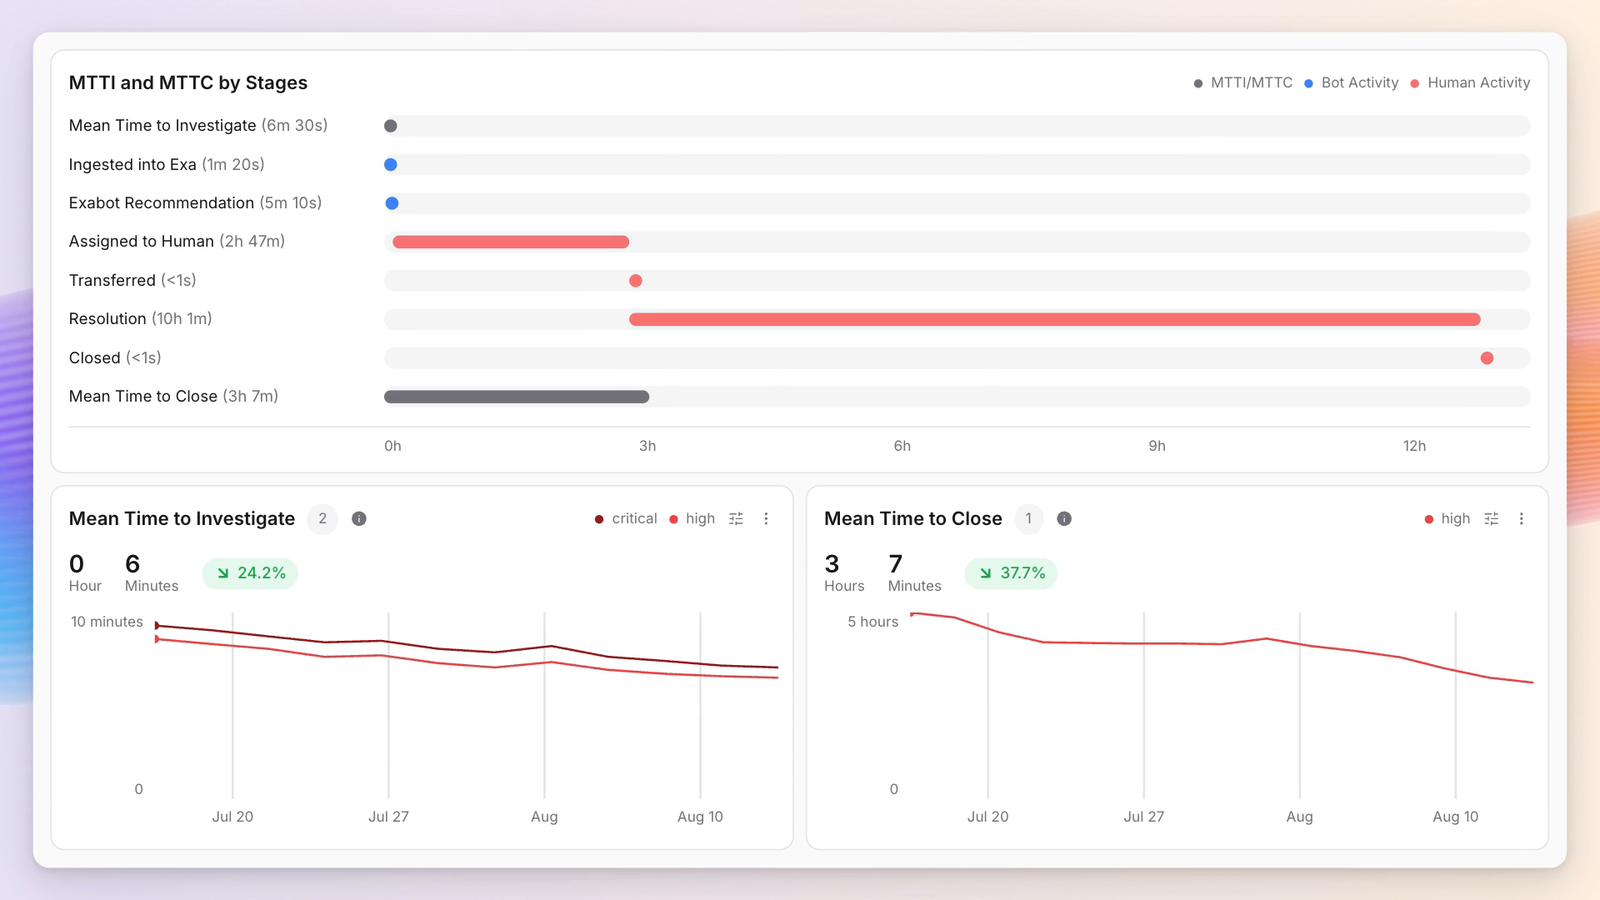
Challenges with legacy MDRs
Noise over outcomes
Traditional MDRs built on legacy tech often forward every “suspicious” alert instead of validating and resolving it, becoming an expensive notification engine that still drains your team’s time and focus.
Outdated coverage
Legacy MDR stacks were built for legacy environments, not modern IaaS, SaaS, and IdP systems, so you pay for “monitoring” that doesn’t understand how your business operates.
Slow to ramp, slower to adapt
Traditional MDRs often fail to understand your evolving business or technology stack, taking weeks to onboard and even longer to get up to speed, leaving threats lingering while the backlog grows.
Black box with unclear value
Lack of transparency makes it difficult to understand how your MDR manages your environment or to confirm results.
With Exaforce, outcomes replace noise. This is what MDR should feel like.
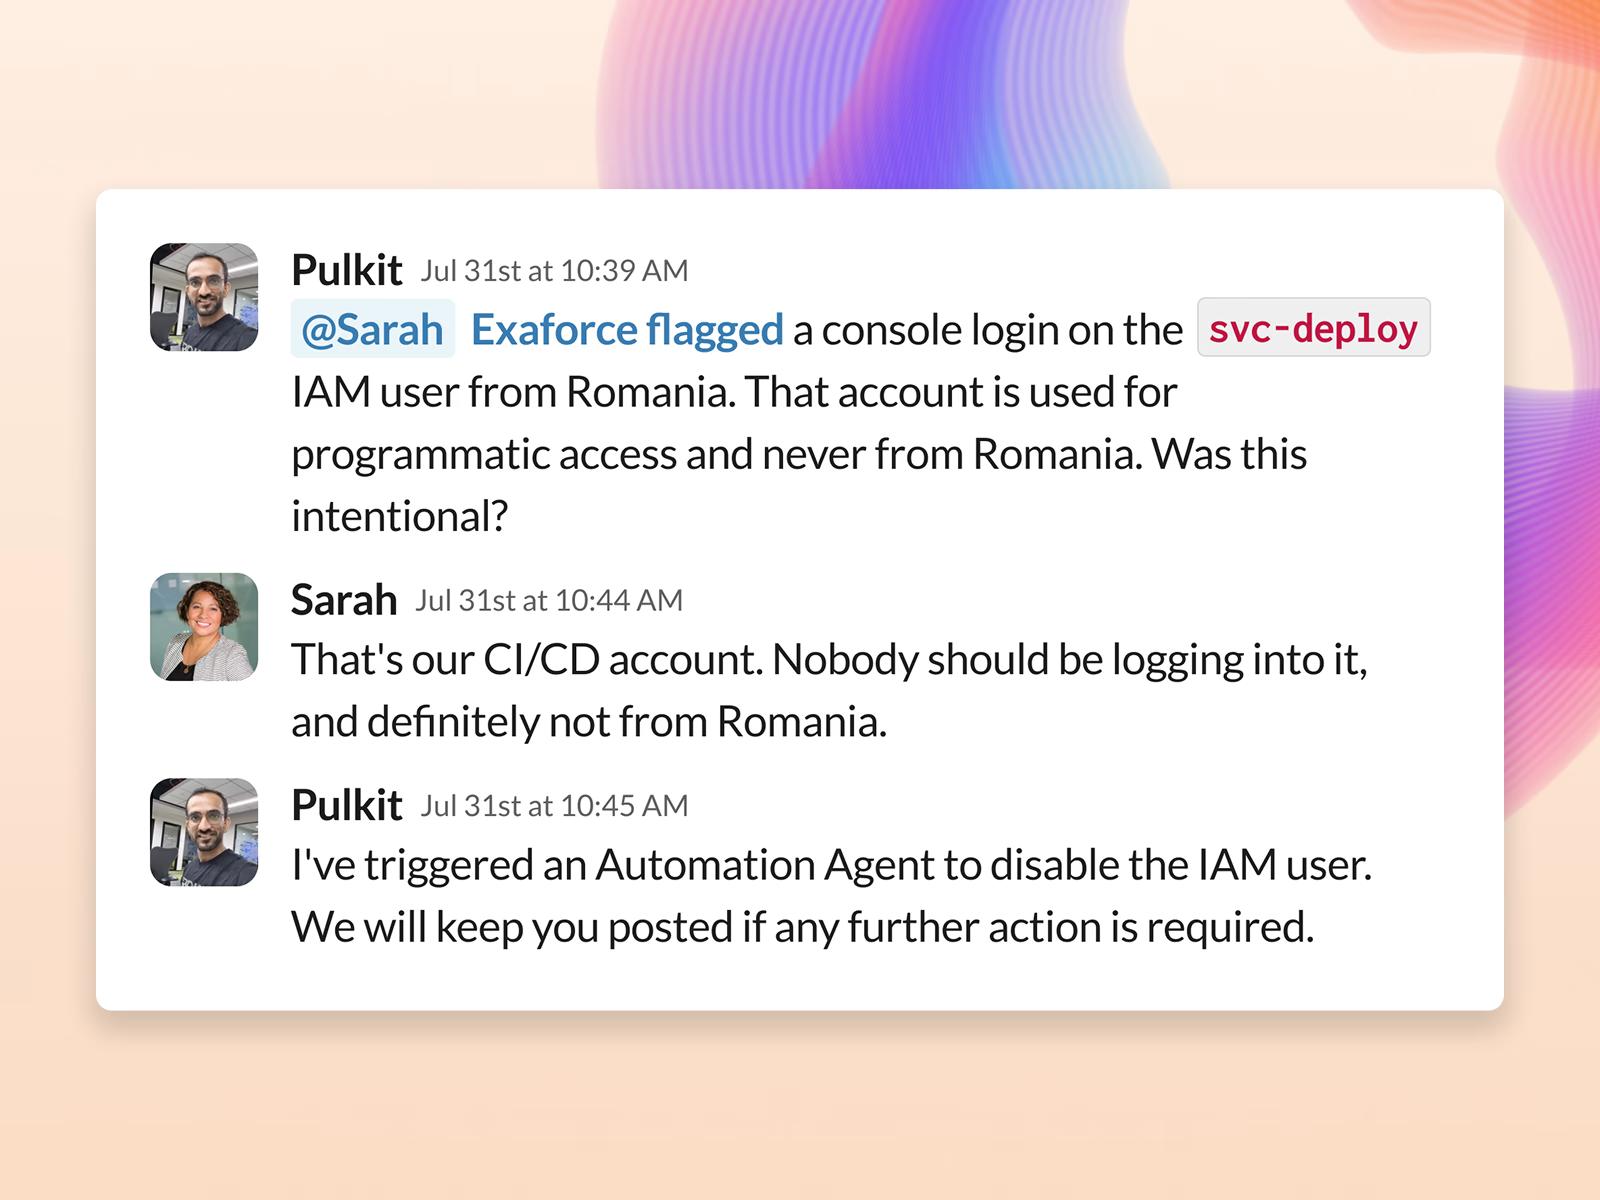
AI-augmented analysts on duty 24x7
The global Exaforce SOC pairs veteran responders with agentic AI to deliver hands-on monitoring, investigation, and containment around the clock, eliminating the need for a follow-the-sun team.
AI-augmented analysts on duty 24x7
The global Exaforce SOC pairs veteran responders with agentic AI to deliver hands-on monitoring, investigation, and containment around the clock, eliminating the need for a follow-the-sun team.
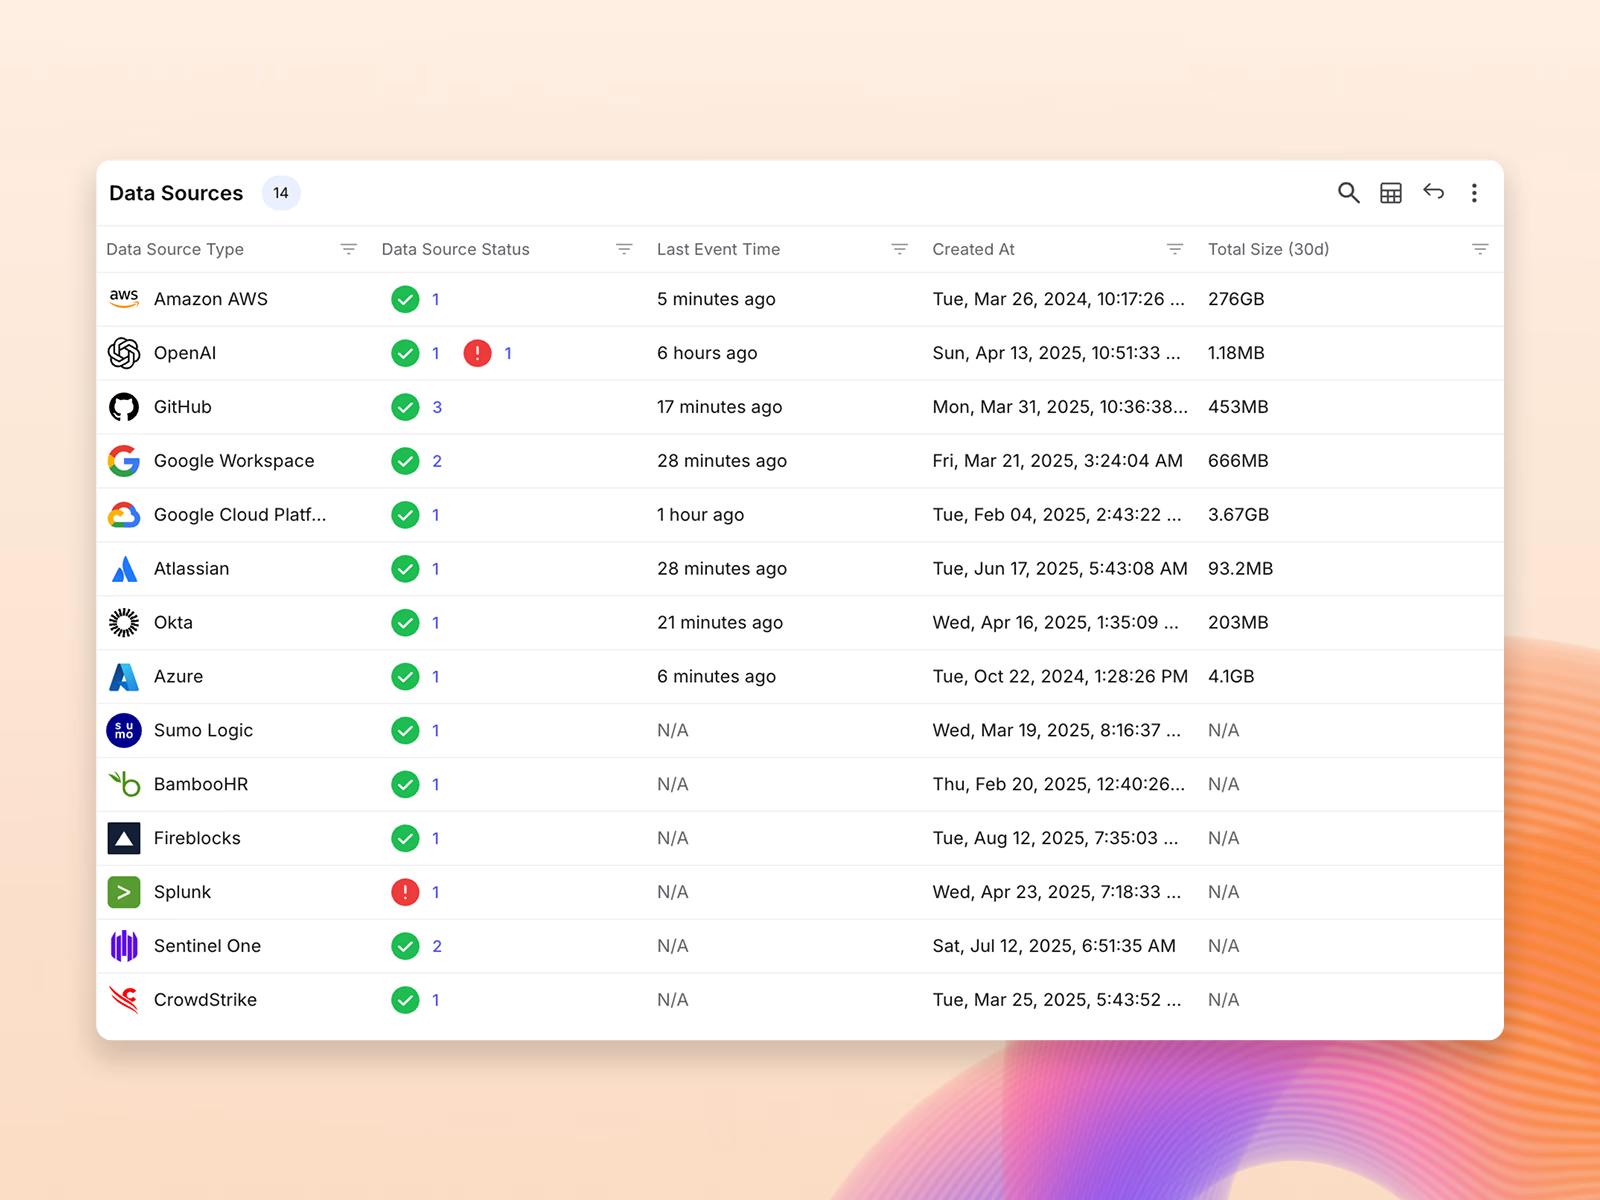
Cloud-first coverage
Highly skilled team backed by a multi-model AI architecture that understands cloud-first resources such as identities, SaaS, IaaS, and endpoints.
Cloud-first coverage
Highly skilled team backed by a multi-model AI architecture that understands cloud-first resources such as identities, SaaS, IaaS, and endpoints.
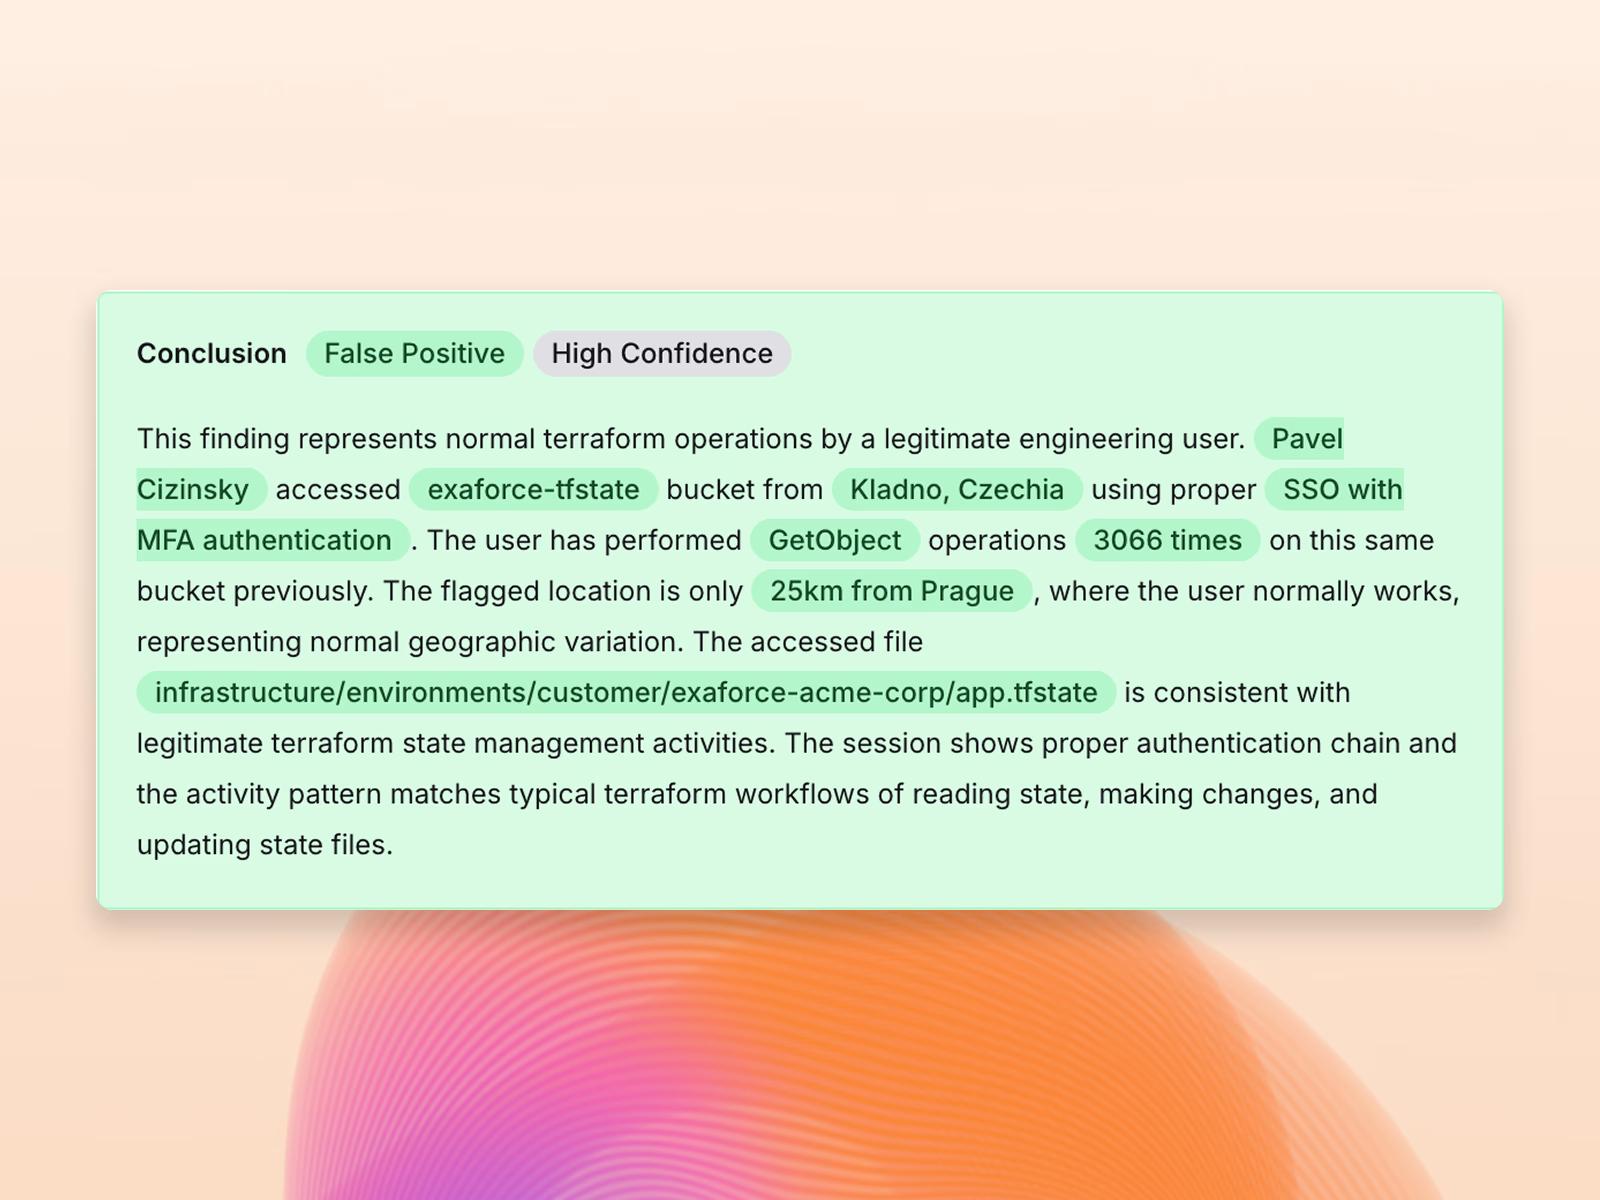
Immediate outcomes, constant evolution
Onboarding within hours with immediate insights into your environment. Our AI continuously learn your environment, while our analysts collect your business context, enabling them to operate like seasoned insiders from day one.
Immediate outcomes, constant evolution
Onboarding within hours with immediate insights into your environment. Our AI continuously learn your environment, while our analysts collect your business context, enabling them to operate like seasoned insiders from day one.
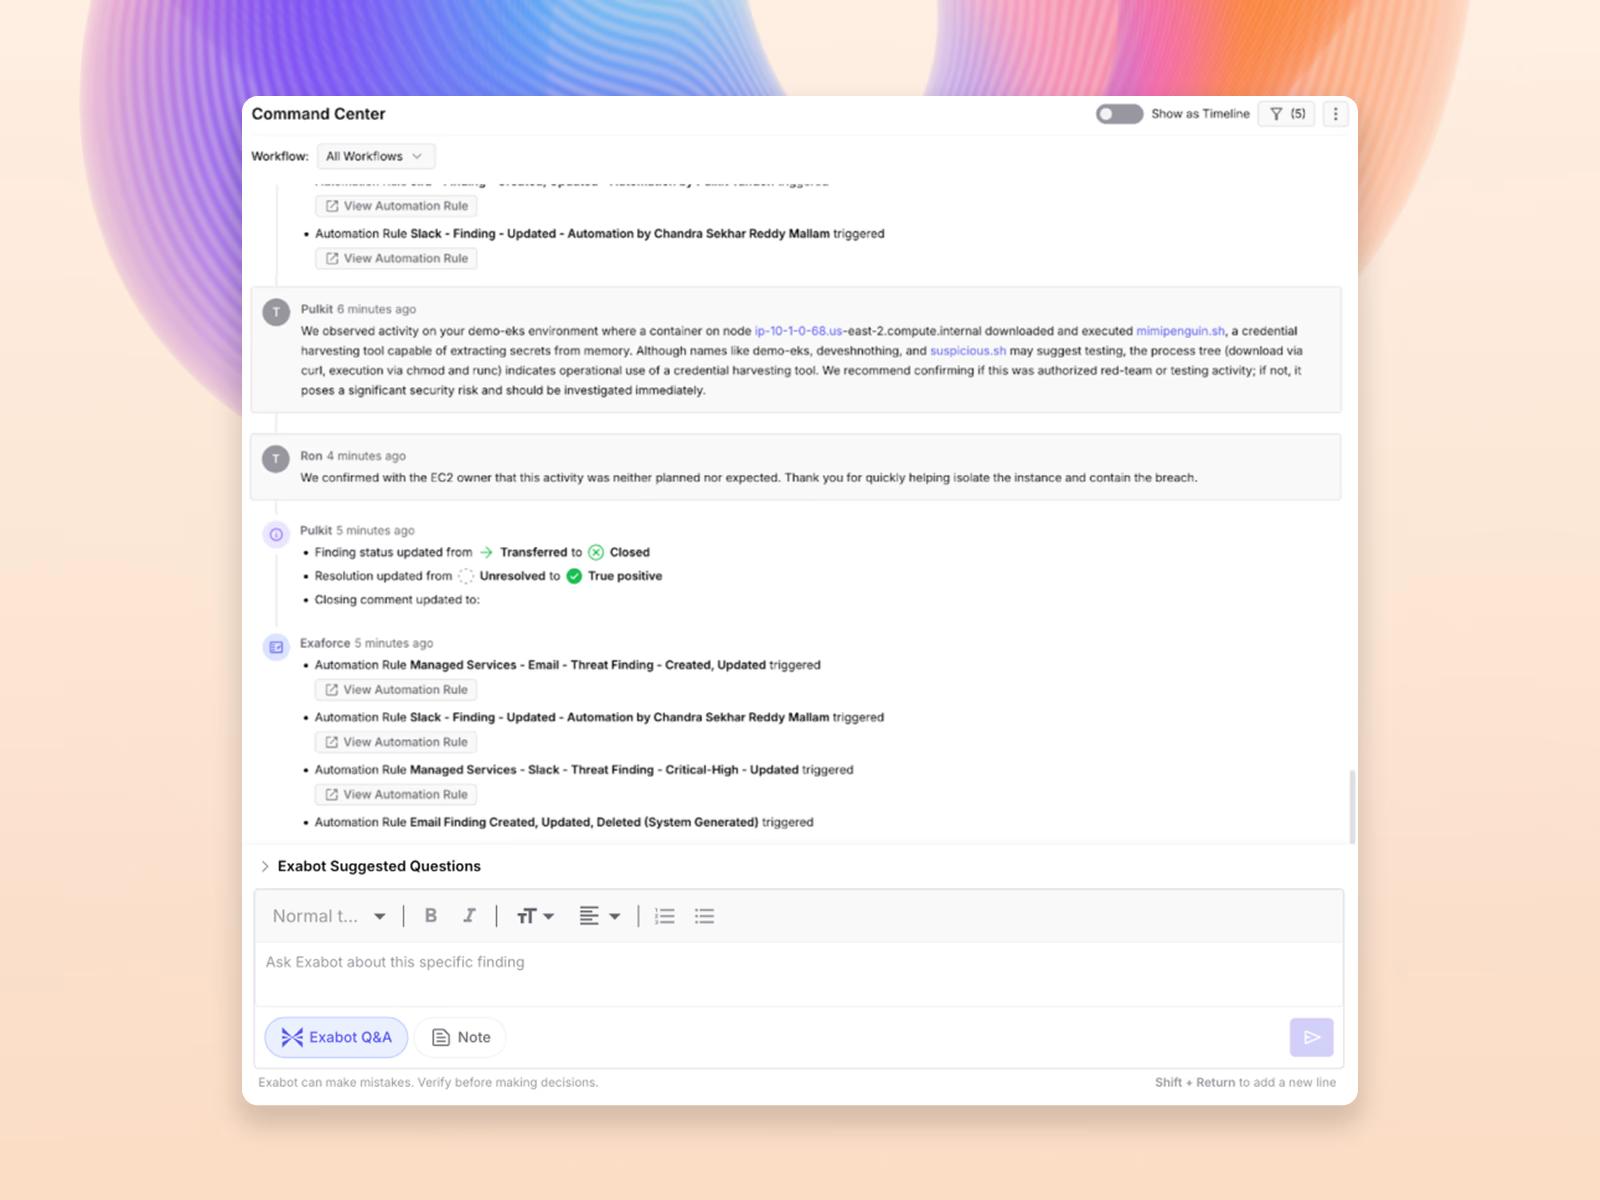
Unified, transparent collaboration
Our team works with you to tailor our coverage to your business while providing full transparent access to the platform and visibility into every alert, decision, and action, complete with continuous updates and executive-ready dashboards.
Unified, transparent collaboration
Our team works with you to tailor our coverage to your business while providing full transparent access to the platform and visibility into every alert, decision, and action, complete with continuous updates and executive-ready dashboards.
Forcepoint
We transitioned from a traditional MSSP model that required significant manual oversight to an MDR platform delivering fully automated, AI‑driven investigation and escalation. This shift fundamentally changed our incident response, reducing timelines from hours or days to minutes and dramatically improving response quality.
CISO at ForcePoint
Frequently asked questions
Do I still have visibility and control with a managed service?
How does Exaforce MDR handle coverage for modern cloud and SaaS environments?
How is Exaforce MDR different from traditional managed detection and response services?
Related resources
Evaluate your AI SOC initiative
A maturity mapped question framework to benchmark AI SOC platforms on detection, triage, investigation, response, and service quality.
Webinar: “What is AI SOC” Anyway?
Cutting through the hype with James Berthoty (CEO & Principal Analyst, Latio) and Taylor Smith (Director of Product, Exaforce)
Latio AI Security Market Report 2025
Get actionable insights about the latest developments in AI security. Written for both security leaders and engineers, this report covers the state of the market, leading use cases, and what vendor innovations.