Log inRequest demo

Exabot Detect

Your AI detection engineer, constantly improving

Exabot Detect learns what's normal in your environment and flags what isn't. It builds and maintains coverage across IaaS, SaaS, identity, code, and collaboration tools, tunes detections, and keeps pace as your stack grows and attackers adapt. No detection engineers required.

Request demo
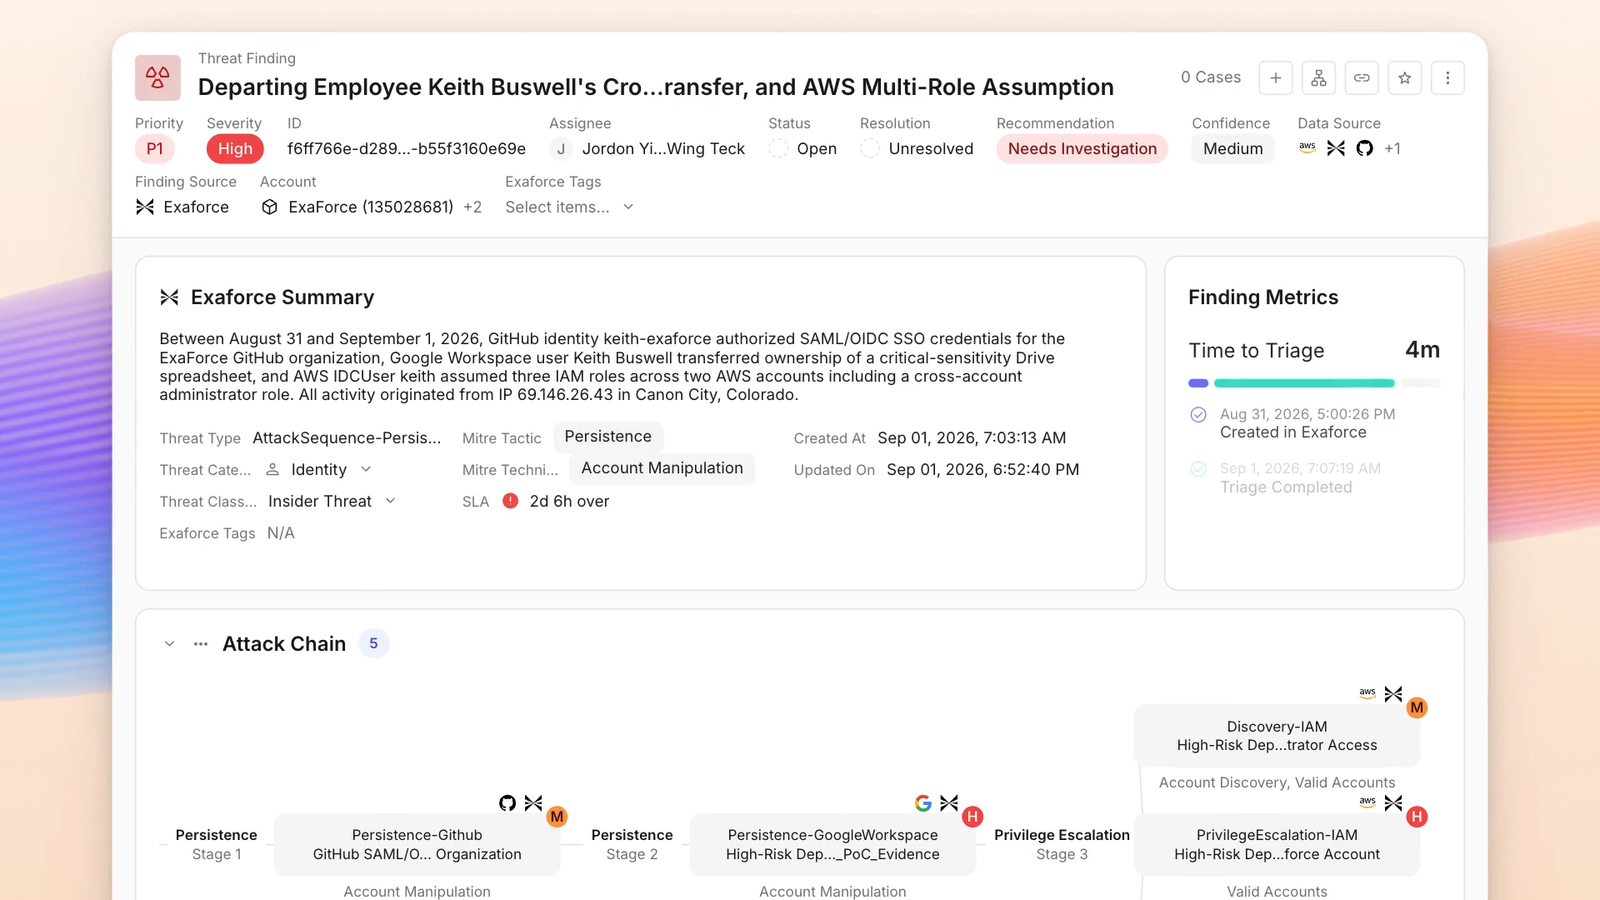
A threat finding showing the Exaforce summary, triage metrics, and the attack chain reconstructed in stages across GitHub, Google Workspace and AWS.

Smarter detection that scales with your business

Exabot Detect expands coverage and sharpens accuracy, catching what others miss. It uses AI to reduce noise and keep pace with AI-driven attackers, so your team stays focused, not overwhelmed.

Broader coverage without the overhead of managing a SIEM

Exabot Detect gives your SOC broader visibility and detection coverage across modern enterprise apps and data, including SaaS, collaboration, and VCS tools often missed by SIEMs. It extends detection to platforms like Google Workspace, Slack, and GitHub, closing blind spots and catching threats where critical business activity happens.
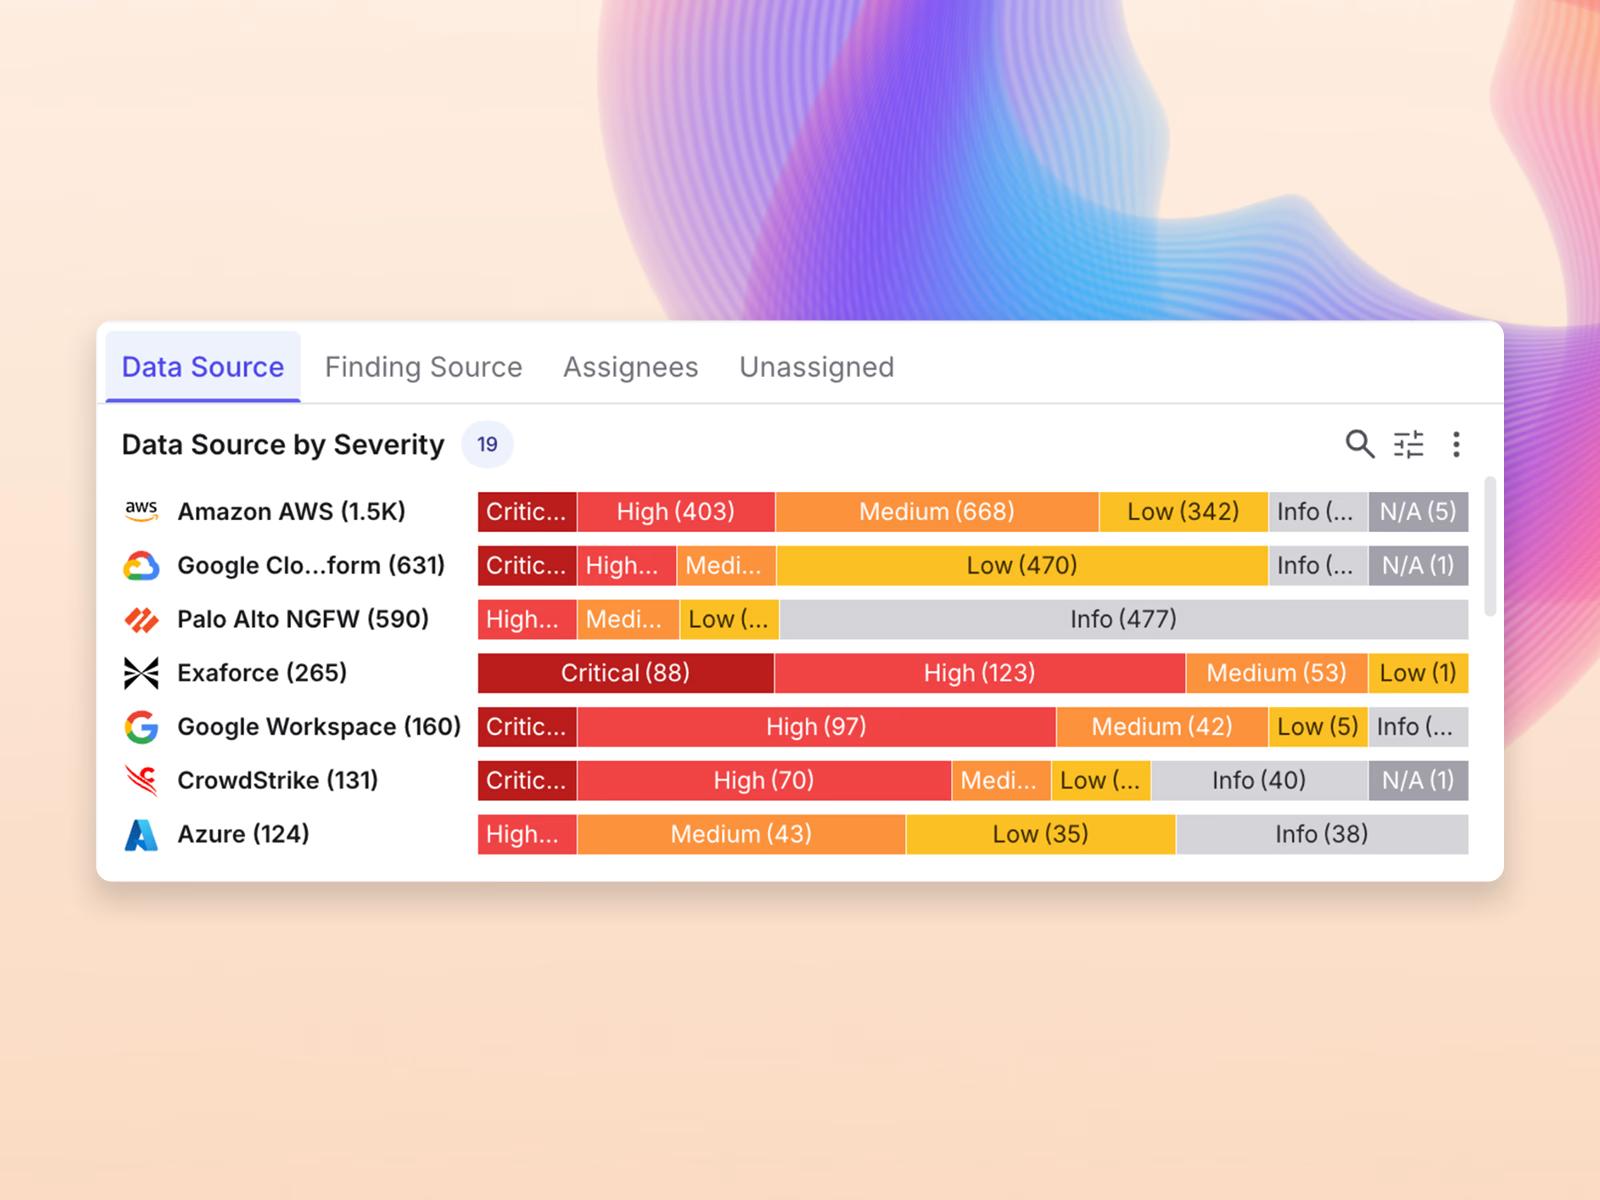
Data source by severity card

Trusted detections you can explain

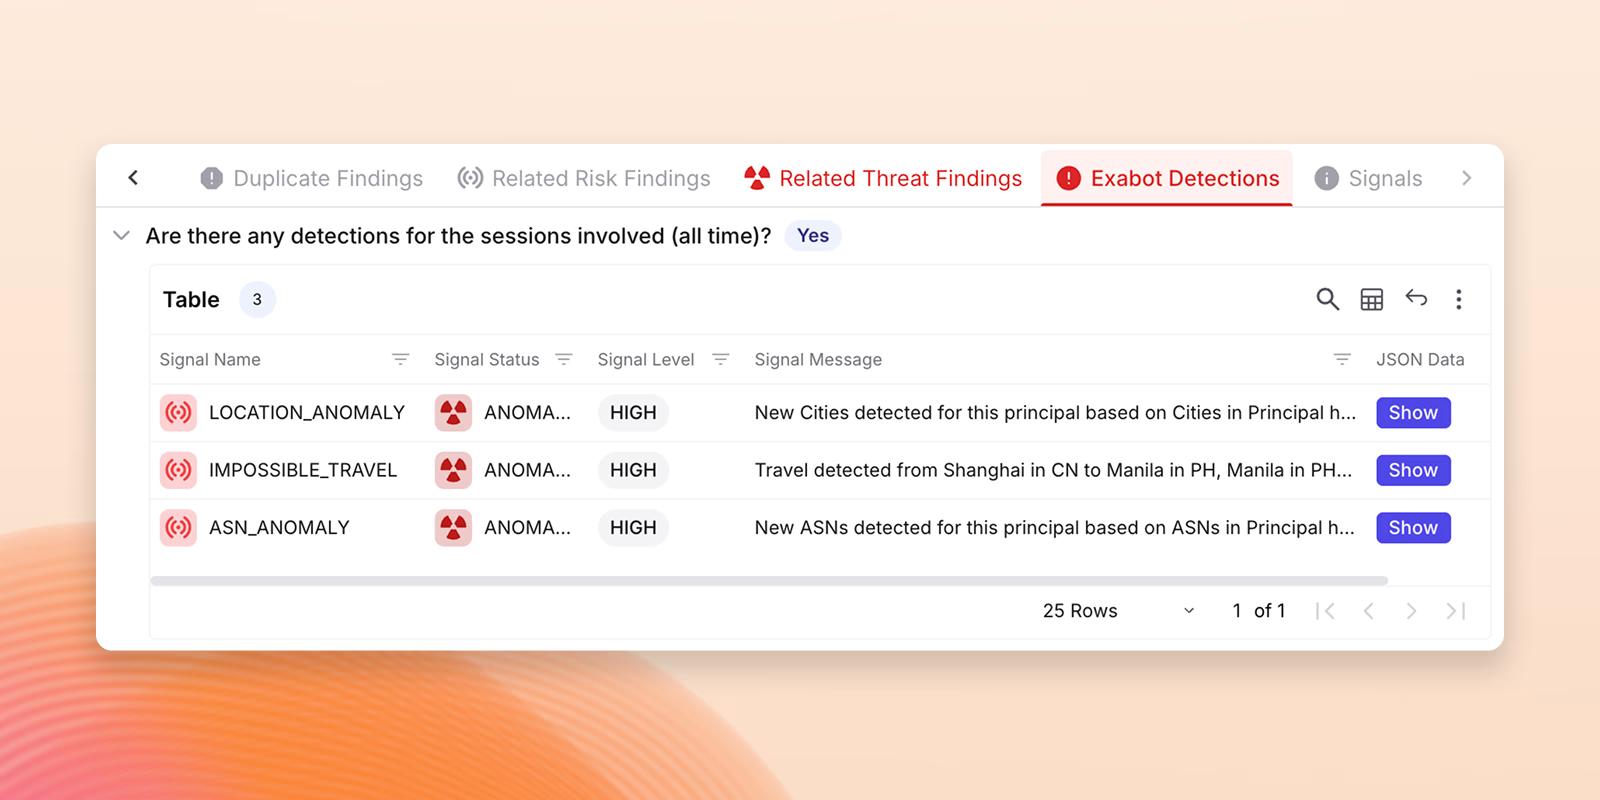
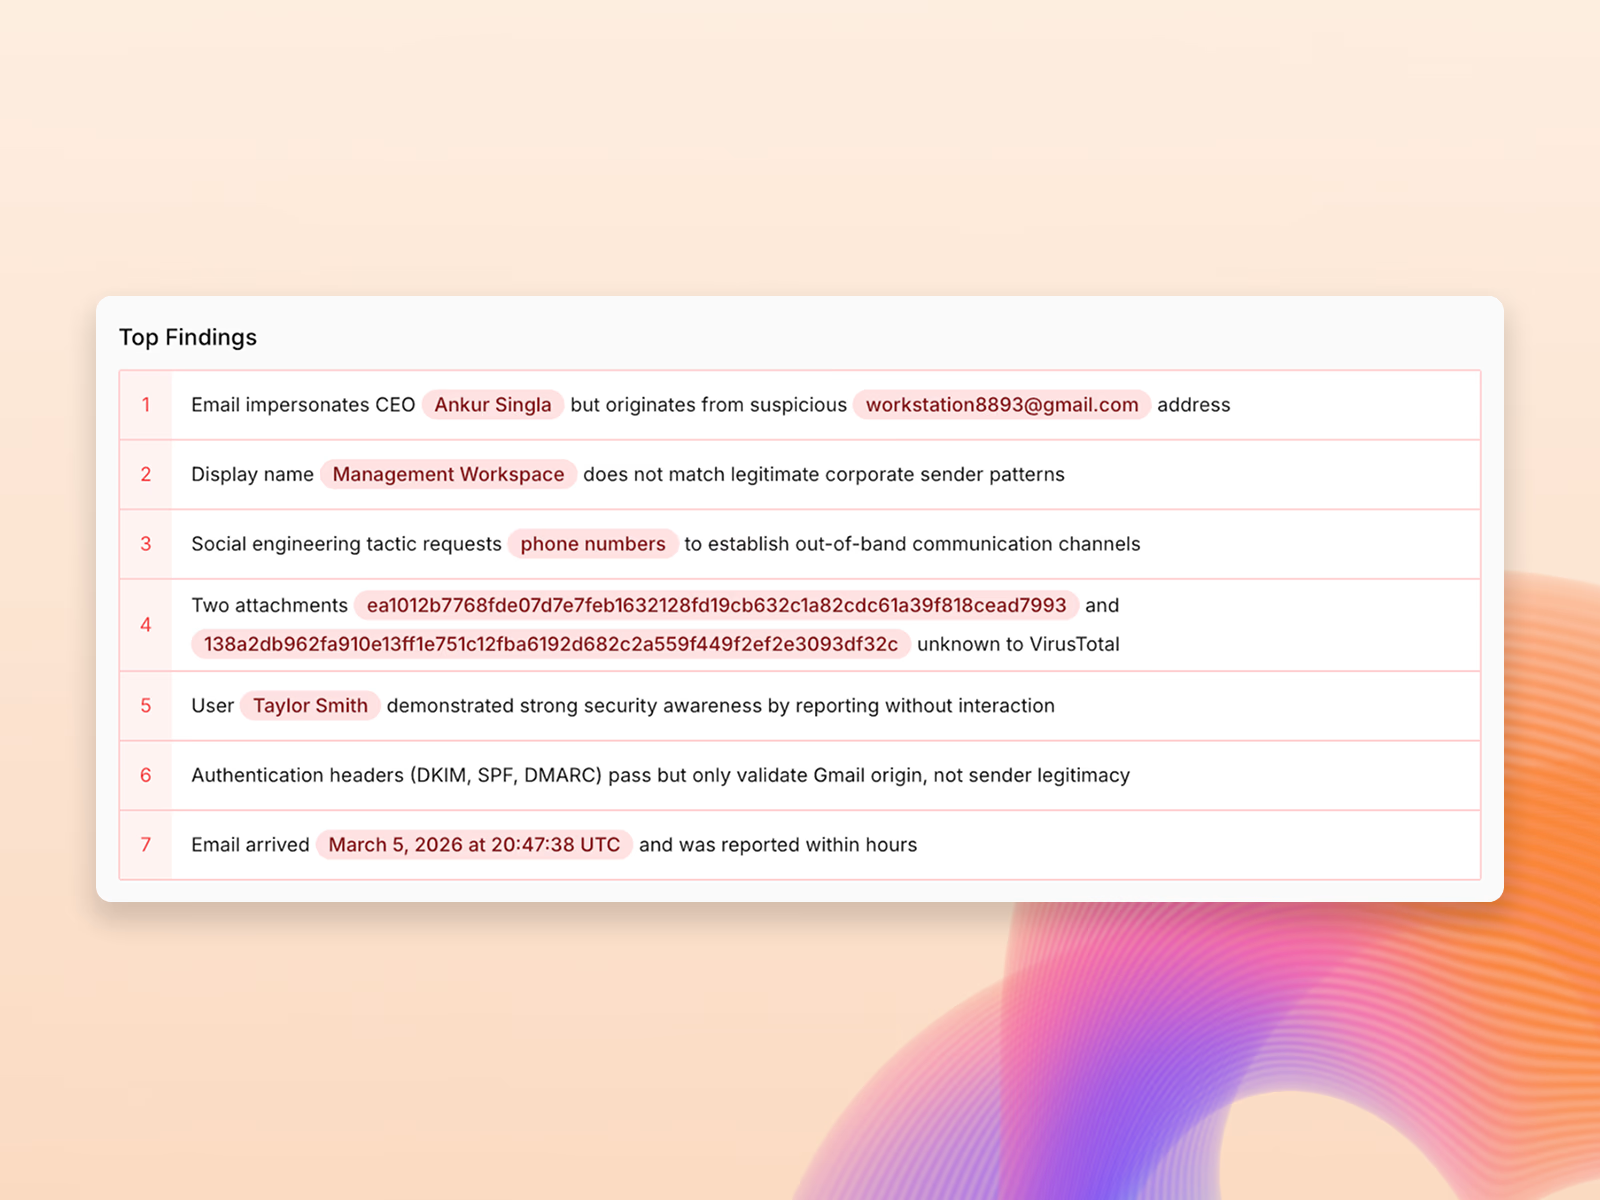
Every Exabot alert comes with clear and defensible reasoning, both in natural language and in data. See the evidence, the context, and the MITRE technique behind each detection, so your analysts and auditors always understand why something was flagged.

Top findings card

Detections that are fully managed, fully custom, or anything in between

Detection technology that meets you where you are, whether you want turnkey coverage or deep customization. Offload tedious rule tuning and complex mechanics so your detection engineering team can focus on real security outcomes, not wrestling with pipelines, logic, or brittle SIEM rules.

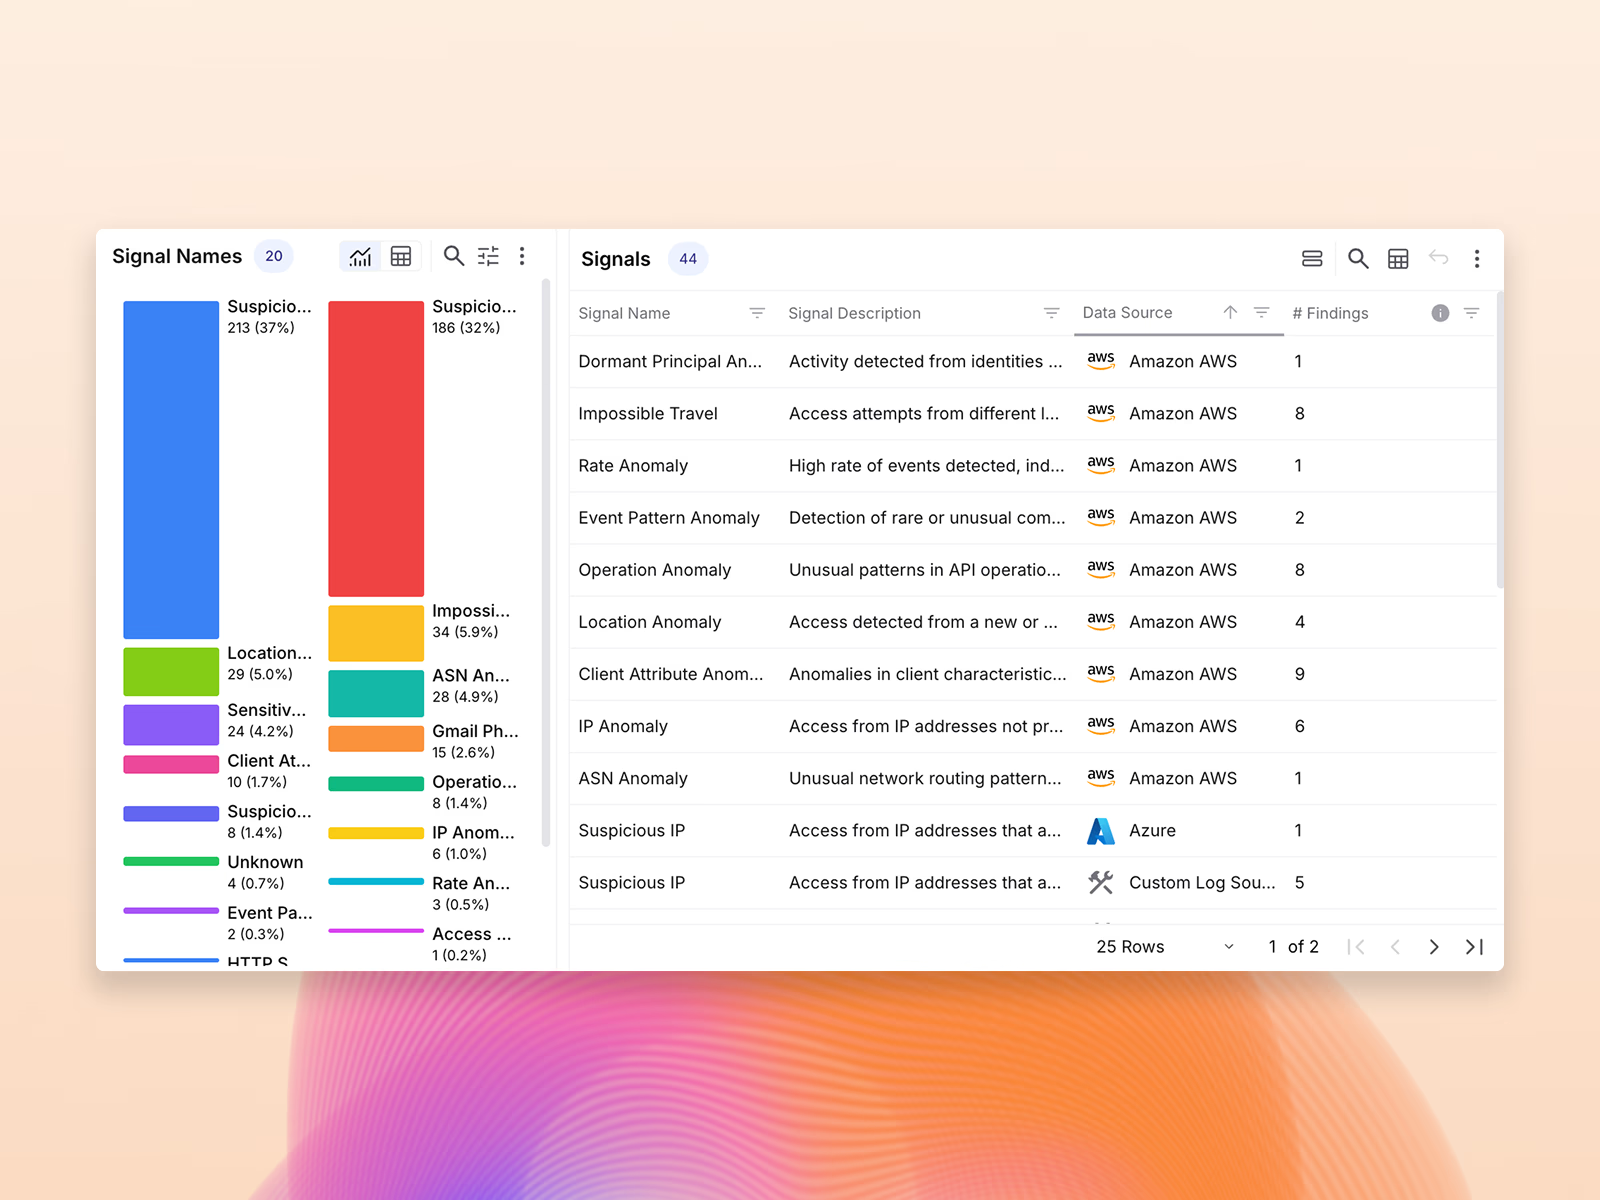
Detection signals card

Multistage detection pipeline that results in high fidelity low volume alerts

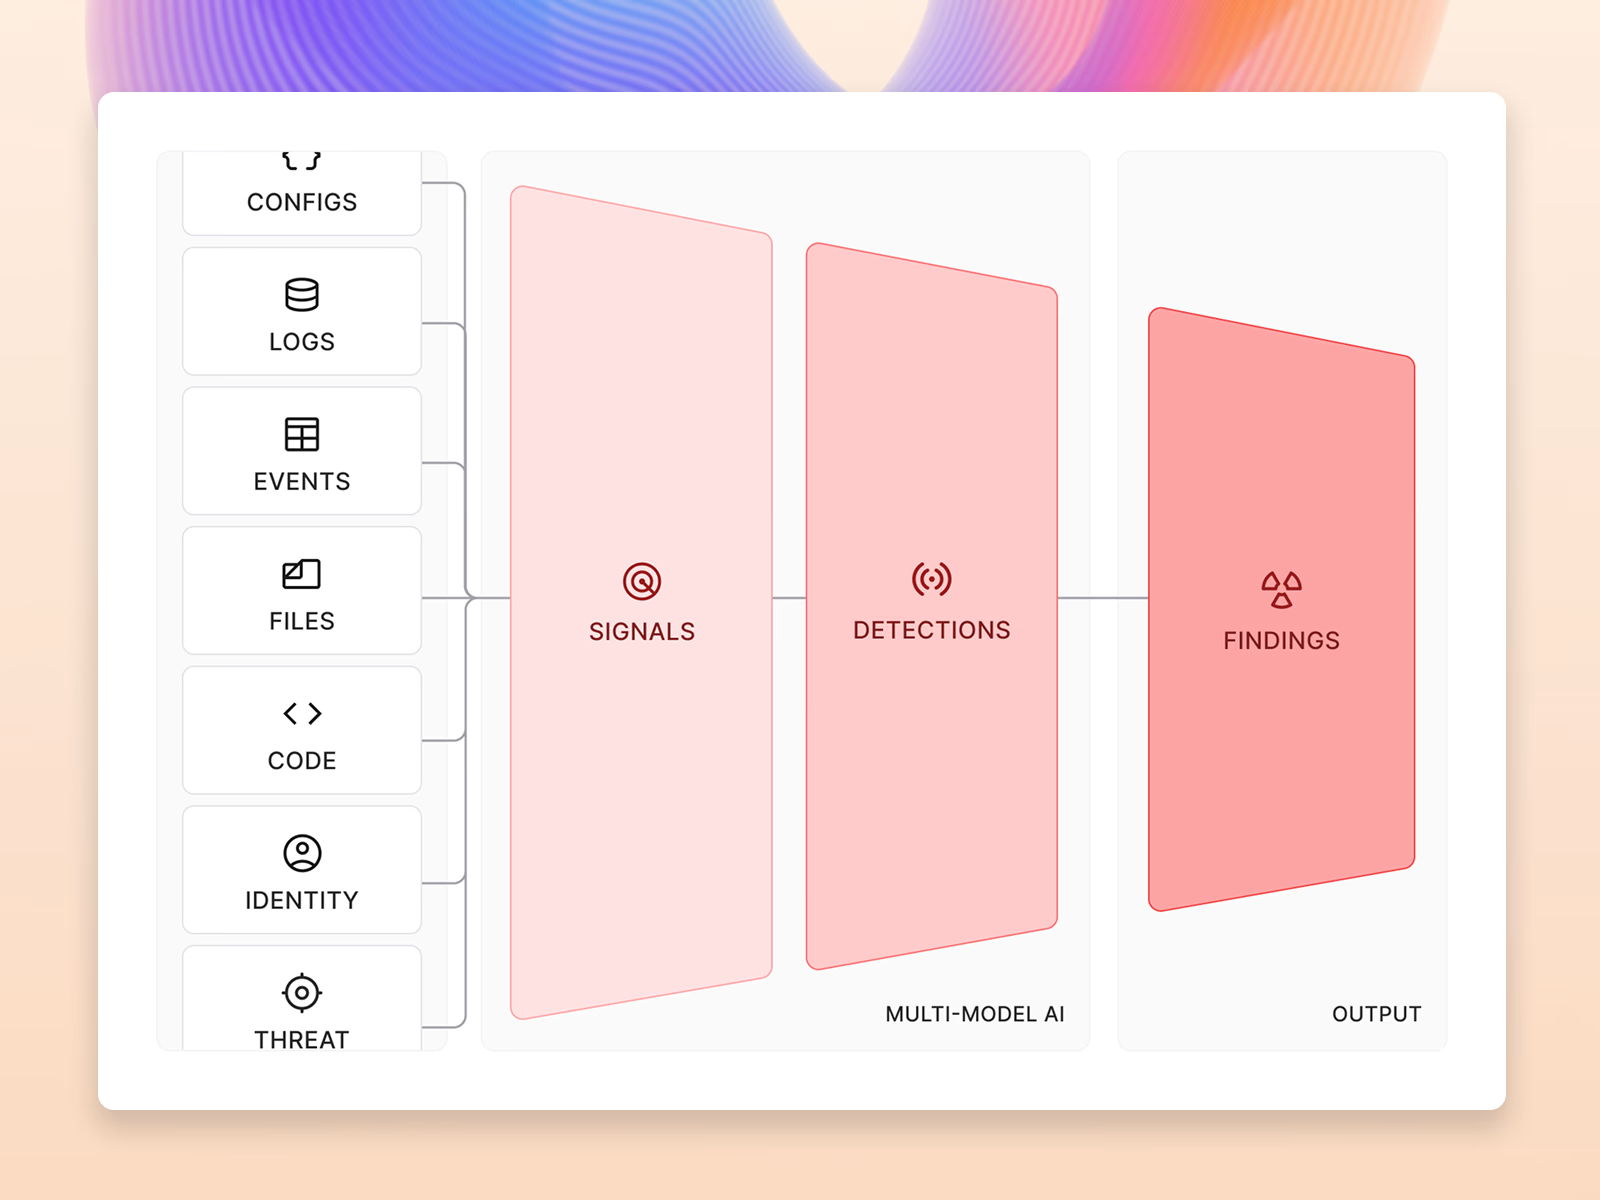
A tiered detection pipeline ingests and correlates low-fidelity signals across users, assets, and apps, then enriches and filters them into a small set of high-confidence alerts your SOC can act on. AI continuously analyzes billions of events, removing noise and benign activity so analysts see only what truly represents risk, even as attackers scale with AI.

Funnel graphic card

Featured detection capabilities

Advanced detection features designed to surface real threats without additional noise.

Machine learning and rule-based detections

Threat Findings based on complex statistical behavioral models, including rate anomalies, peer analysis, and more, coupled with rule-based detections.

Curated data dashboard to substantiate the detection

Fortify your understanding and each alert with data as evidence provided in a curated dashboard.

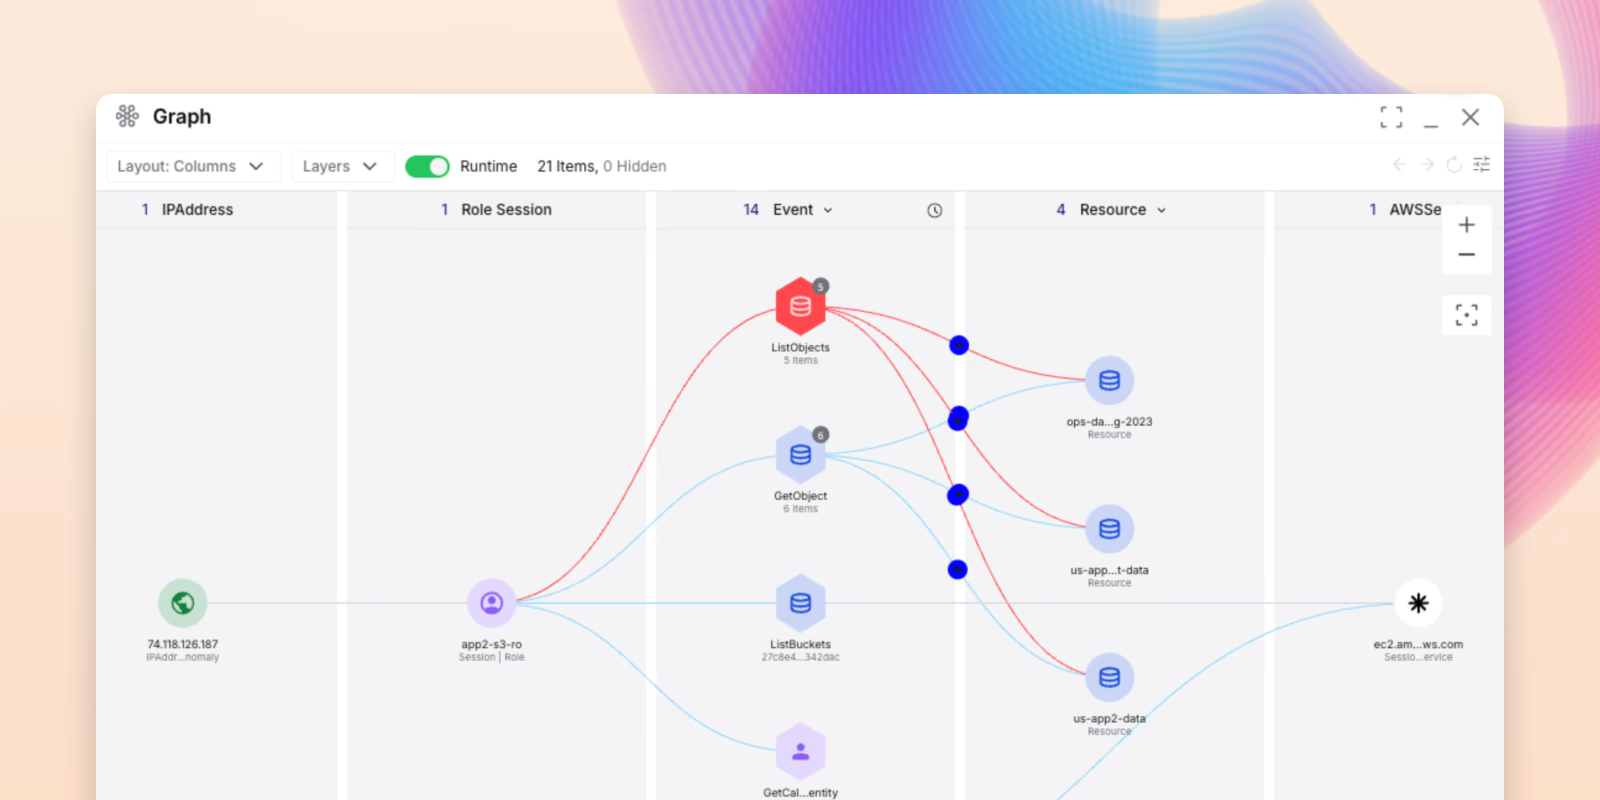
Threat Finding Graph

Show the relationships between actors, actions, and resources in an intuitive visual.

Accton

Exaforce has significantly improved our SOC efficacy by augmenting threat detection and response for AWS and Azure with AI. Its auto-triage of third-party alerts and rule-free detection streamlines our response and saves us dozens of hours, letting our team focus on mitigating threats, while their exploration capabilities offer greater visibility into all our Cloud services.

Paul Kim

CISO & CIO at Accton

Read case study

Frequently asked questions

Can Exaforce replace or augment SIEM alerts?
Yes, the Exaforce platform's capabilities like Exabot Detect, Exabot Investigate, and our Data Platform covers many of the detections that a SIEM would have for traditional systems and some that many SIEMs do not like GitHub, GWS, and more. These can replace or augment (such as adding detection coverage where SIEM's don't have coverage) an existing SIEM.
Can I add custom detections for threats specific to my environment?
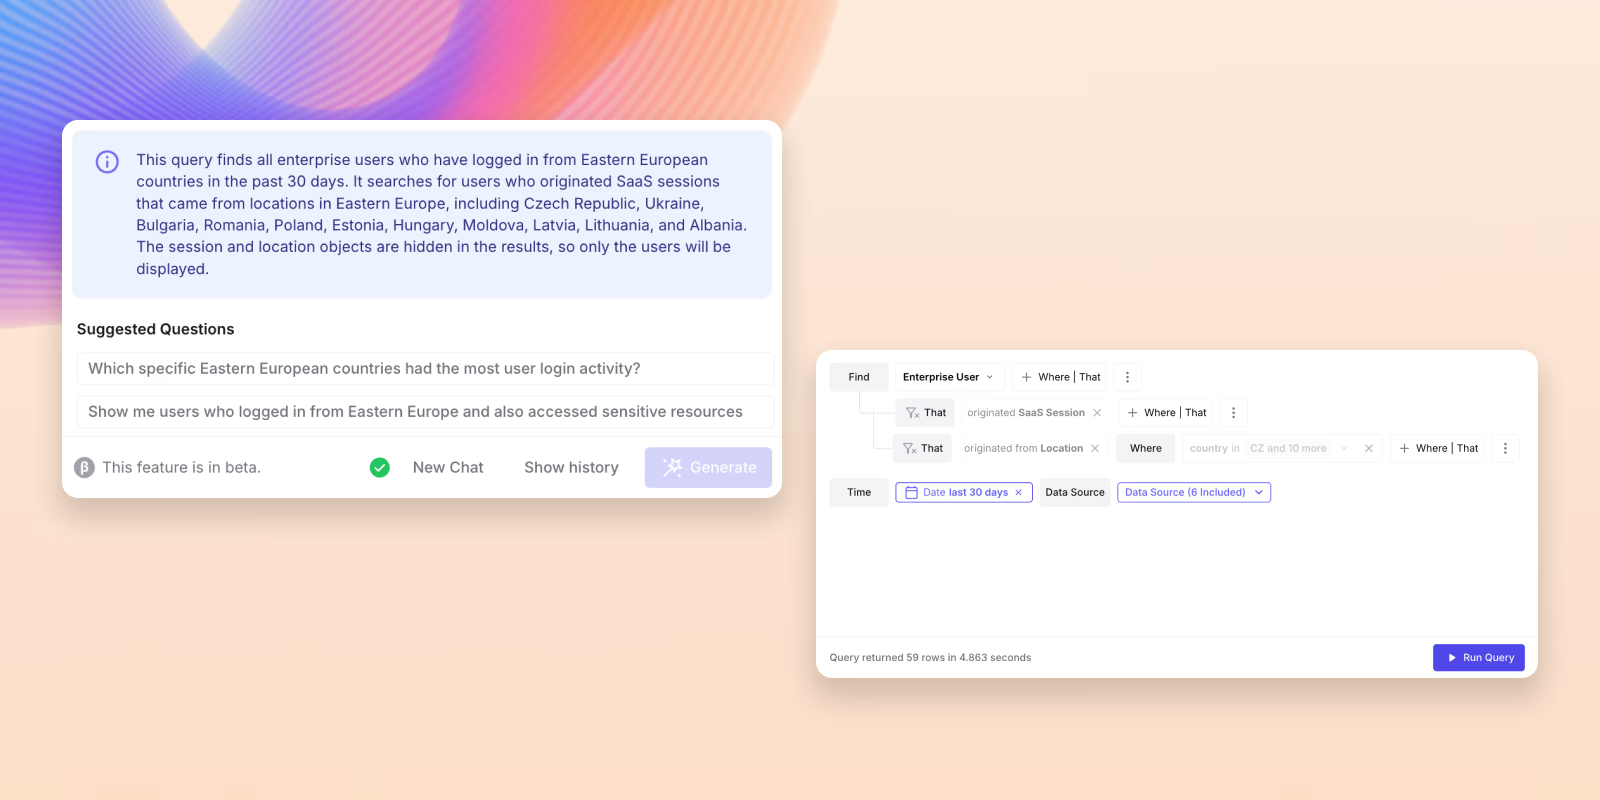
Yes, while Exabot Detect provides comprehensive out-of-the-box detections, you can add organization-specific detection logic using our visual Query Builder or in natural language.
How does Exabot Detect differ from UEBA-like technologies?
Traditional UEBA was built for human users in on-premises environments and struggles with modern cloud entities such as IAM roles, service principals, federated identities, machine accounts, and AI agents. Exabot Detect uses purpose-built AI/ML models that understand cloud-native identity constructs and track hundreds of behavioral features simultaneously (geographic + temporal + volumetric + resource + peer group patterns) rather than UEBA's limited single-dimensional baselines. This multi-dimensional approach catches sophisticated threats targeting cloud infrastructure while dramatically reducing false positives from legitimate cloud automation.
How does Exabot Detect reduce alert fatigue?
Exabot Detect excels at detecting sophisticated threats in cloud and SaaS environments, such as credential compromise (impossible travel, anomalous authentication patterns, session hijacking), insider threats (data exfiltration by departing employees, abnormal access to sensitive resources), cloud misuse (privilege escalation, unauthorized resource creation, policy violations), SaaS abuse (mass file downloads, unusual sharing patterns, admin role changes). Multi-dimensional behavioral analysis catches attacks that blend into normal cloud activity. These are scenarios where rule-based detections generate excessive false positives or miss threats entirely.
How is Exabot Detect different from traditional detection tools?
Exabot Detect provides detection and response capabilities for critical cloud and SaaS sources similar to how EDR protects endpoints. Our Semantic Model's deep integration with AWS, GCP, GitHub, Okta, Google Workspace, and many other platforms enables sophisticated AI/ML-based threat detection using data from our Behavioral Model’s ability to track anomalies across identity, resource, and activity dimensions that traditional tools miss. Every detection is automatically triaged using our Knowledge Model with business context consideration, clear disposition recommendations, and supporting evidence, delivering high-fidelity alerts and not just alerts requiring manual investigation.
How much tuning do I have to do to improve Exabot Detections?
There is minimal tuning required. Exabot Detect findings are automatically triaged like any third-party alert, benefiting from all our triage capabilities. Historical analysis, expert analysis, and Business Context Rules applied during triage reduce false positives specific to your environment (lab activity, maintenance windows, expected contractor behavior). Every detection includes clear disposition recommendations with supporting evidence and explanation. As analysts provide feedback on verdicts, the system learns and improves over time. Unlike traditional detection engineering that requires continuous rule writing and tuning, Exabot adapts automatically, focusing on investigating real threats, not maintaining detection logic.