
Exabots
A complete SOC team, always on
A SOC needs detection engineers, triage analysts, threat hunters, and incident responders. Four Exabots cover every role, 24/7, reasoning over one real-time view of your environment.
Trusted by leading security teams


Four Exabots, four roles
Each Exabot owns one role and work as one team reasoning over the same correlated data.
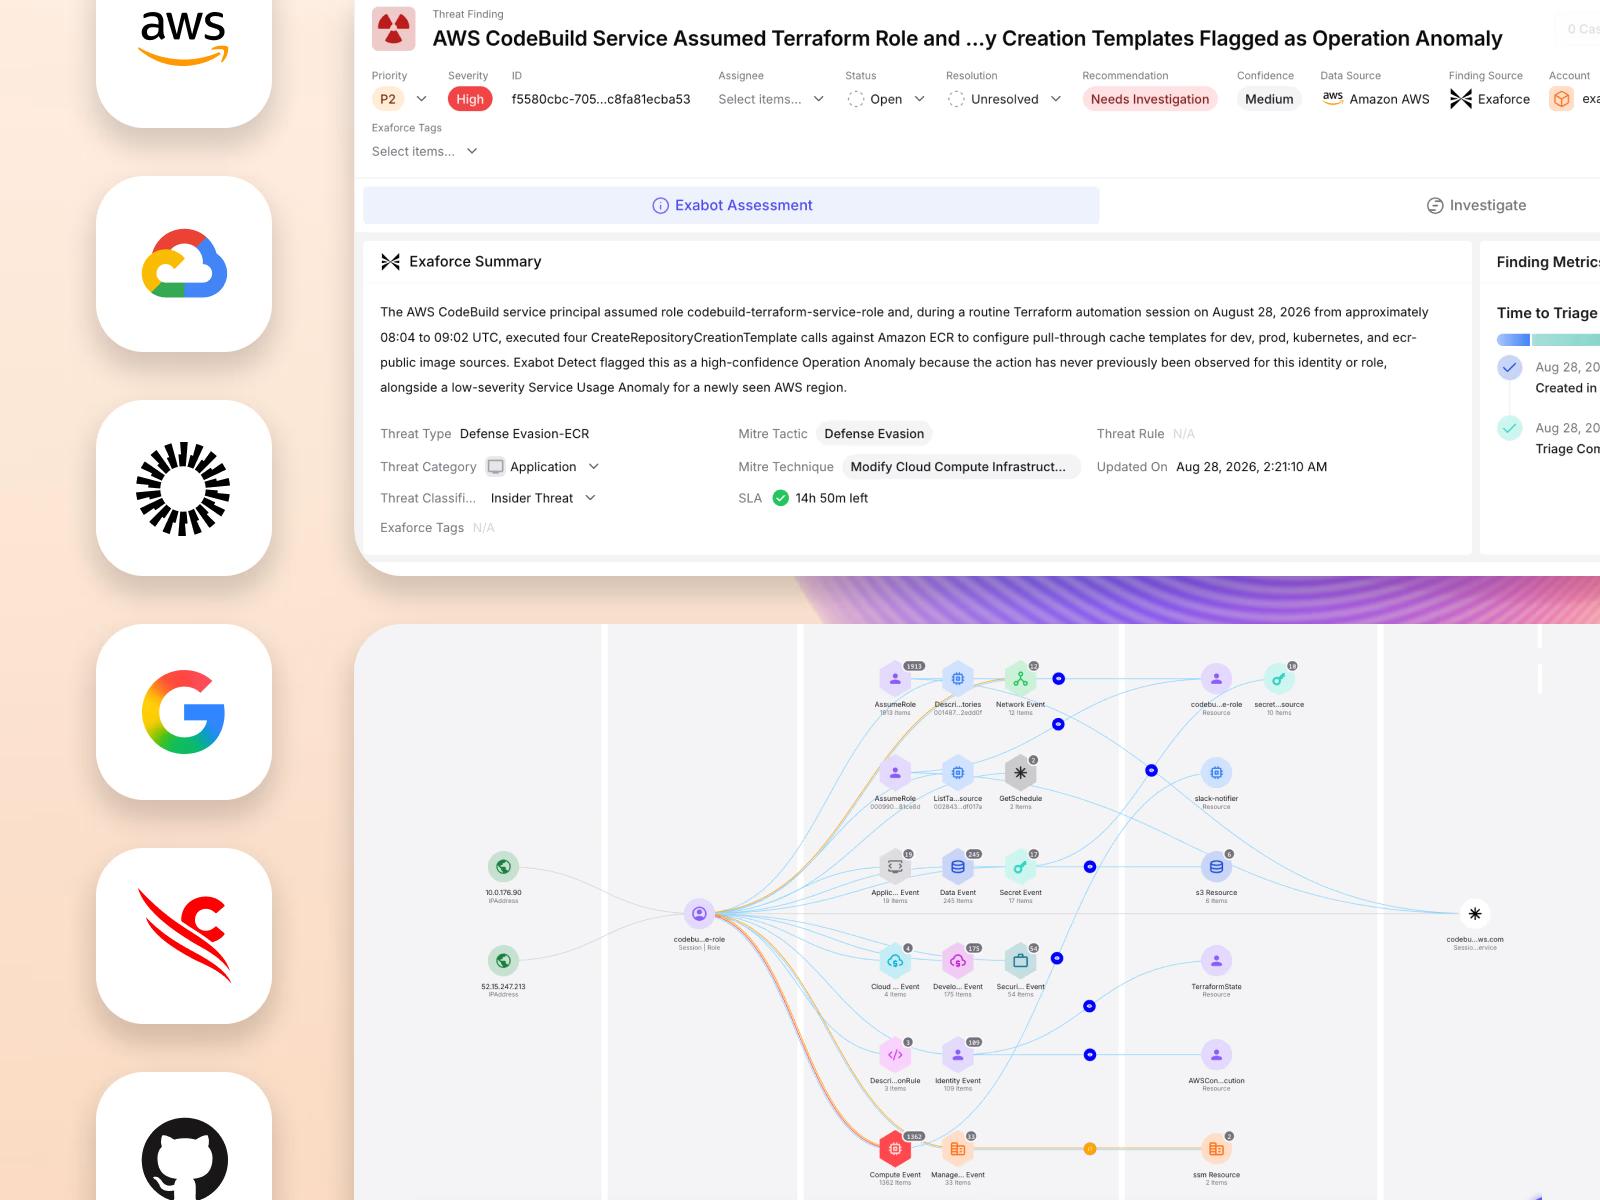
Your AI detection engineer. Learns what's normal across identity, cloud, SaaS, and code, including sources most platforms miss, like GitHub and Google Workspace. Ships with 800+ threat/anomaly condition combinations out of the box. No detection engineering required.
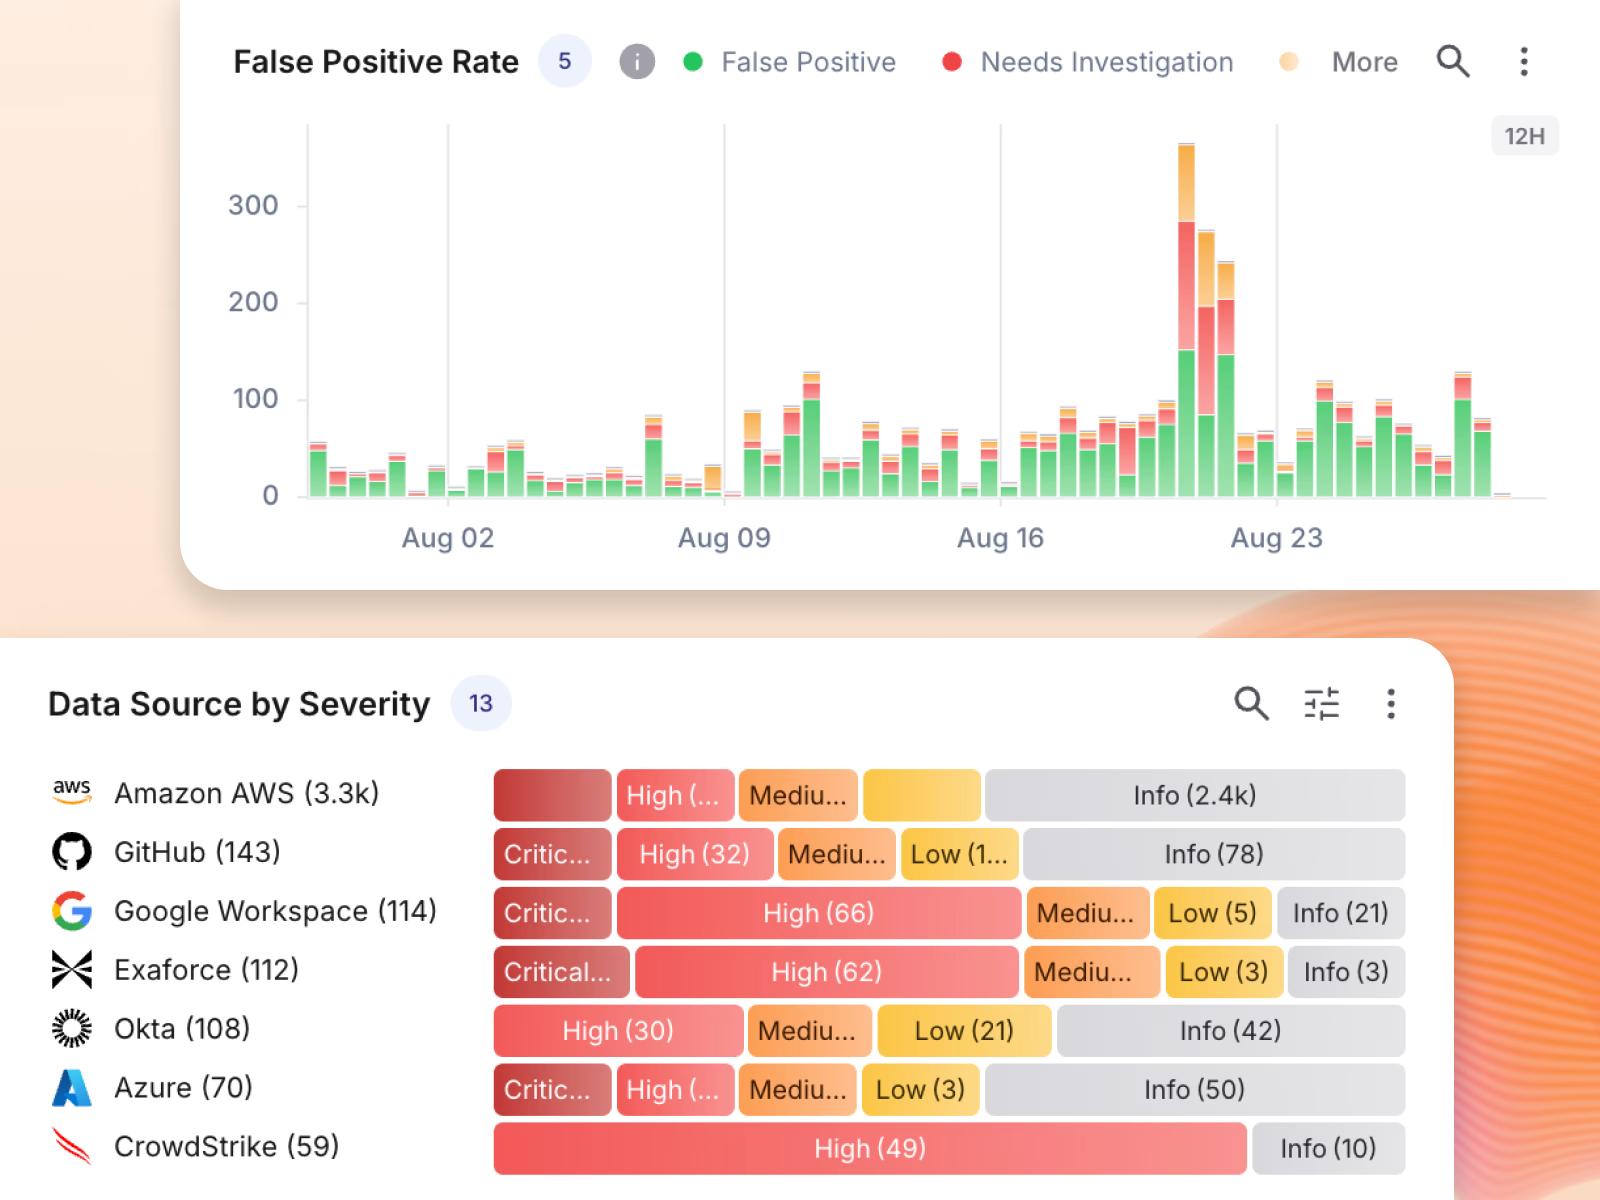
Your AI tier 3 analyst. Investigates every alert at tier 3 depth. False positives filtered out before your team ever sees them, real threats escalated with the evidence attached. A 90% reduction in false positives.
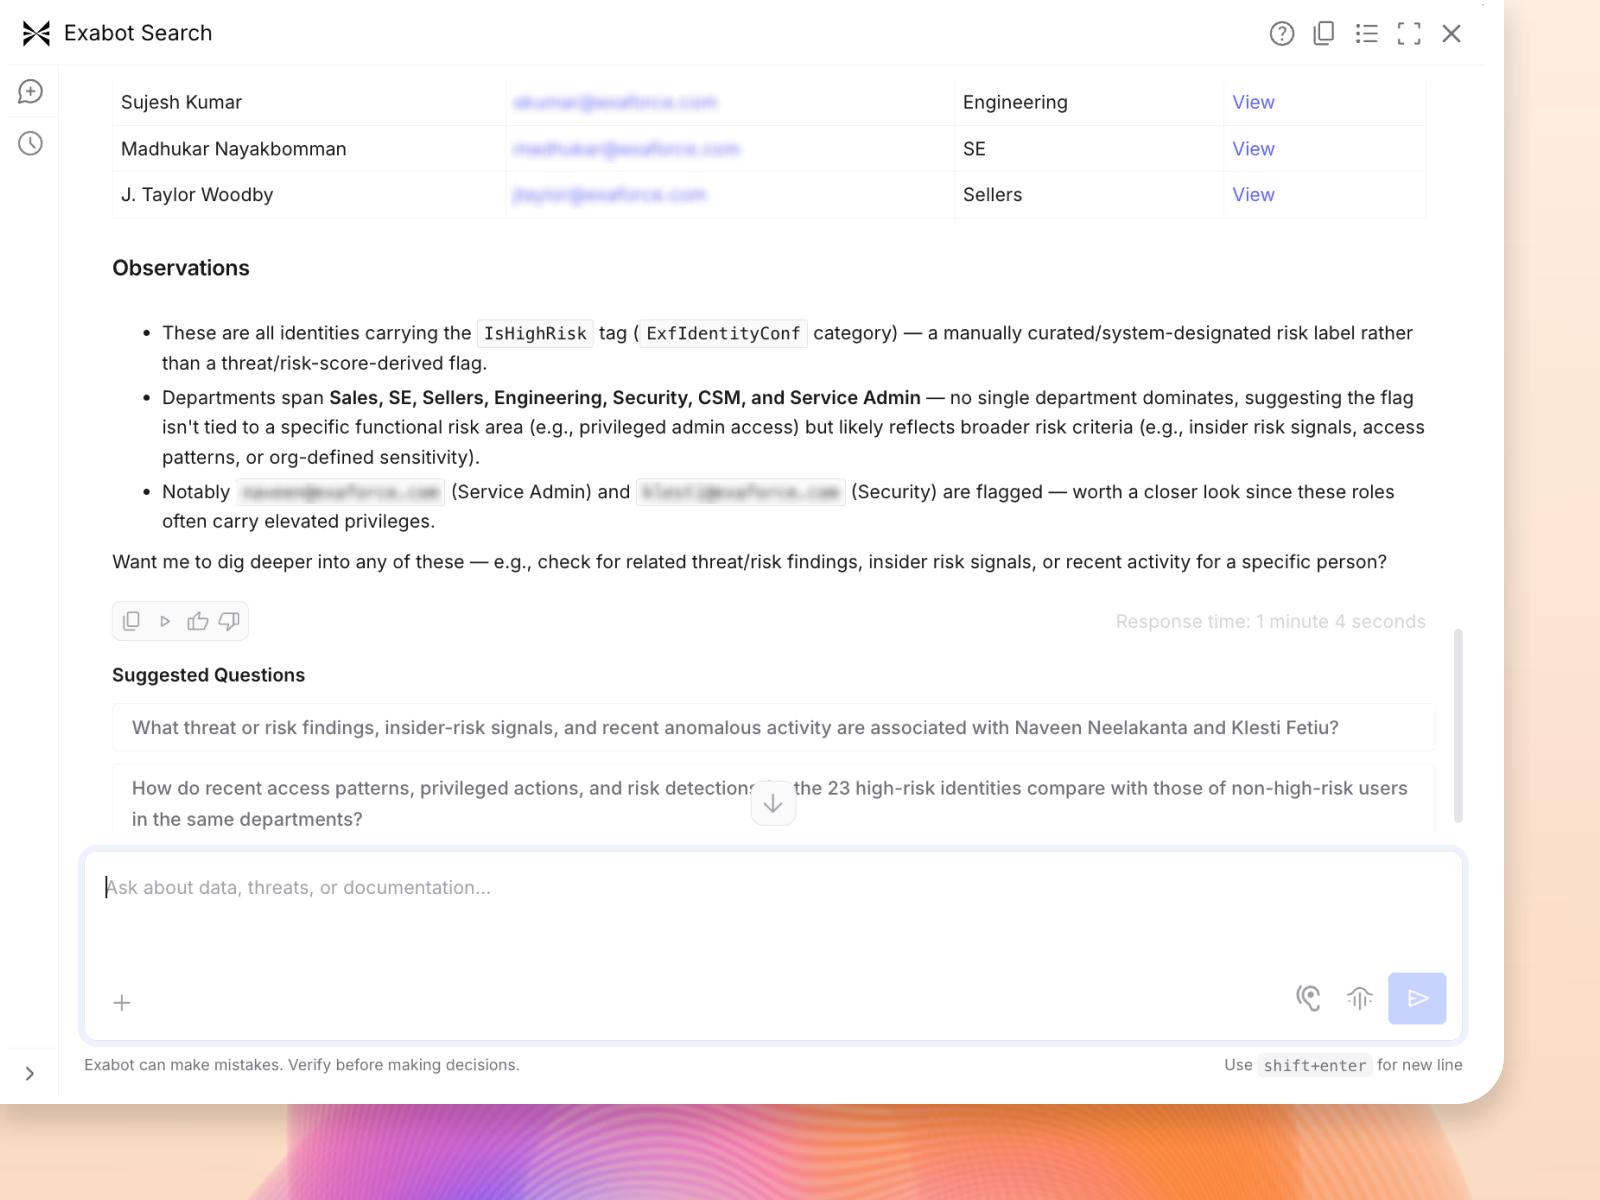
Your AI threat hunter. Takes a question, not a query, so no one hunts across five tools to piece together what happened. A 95% reduction in mean time to investigate.
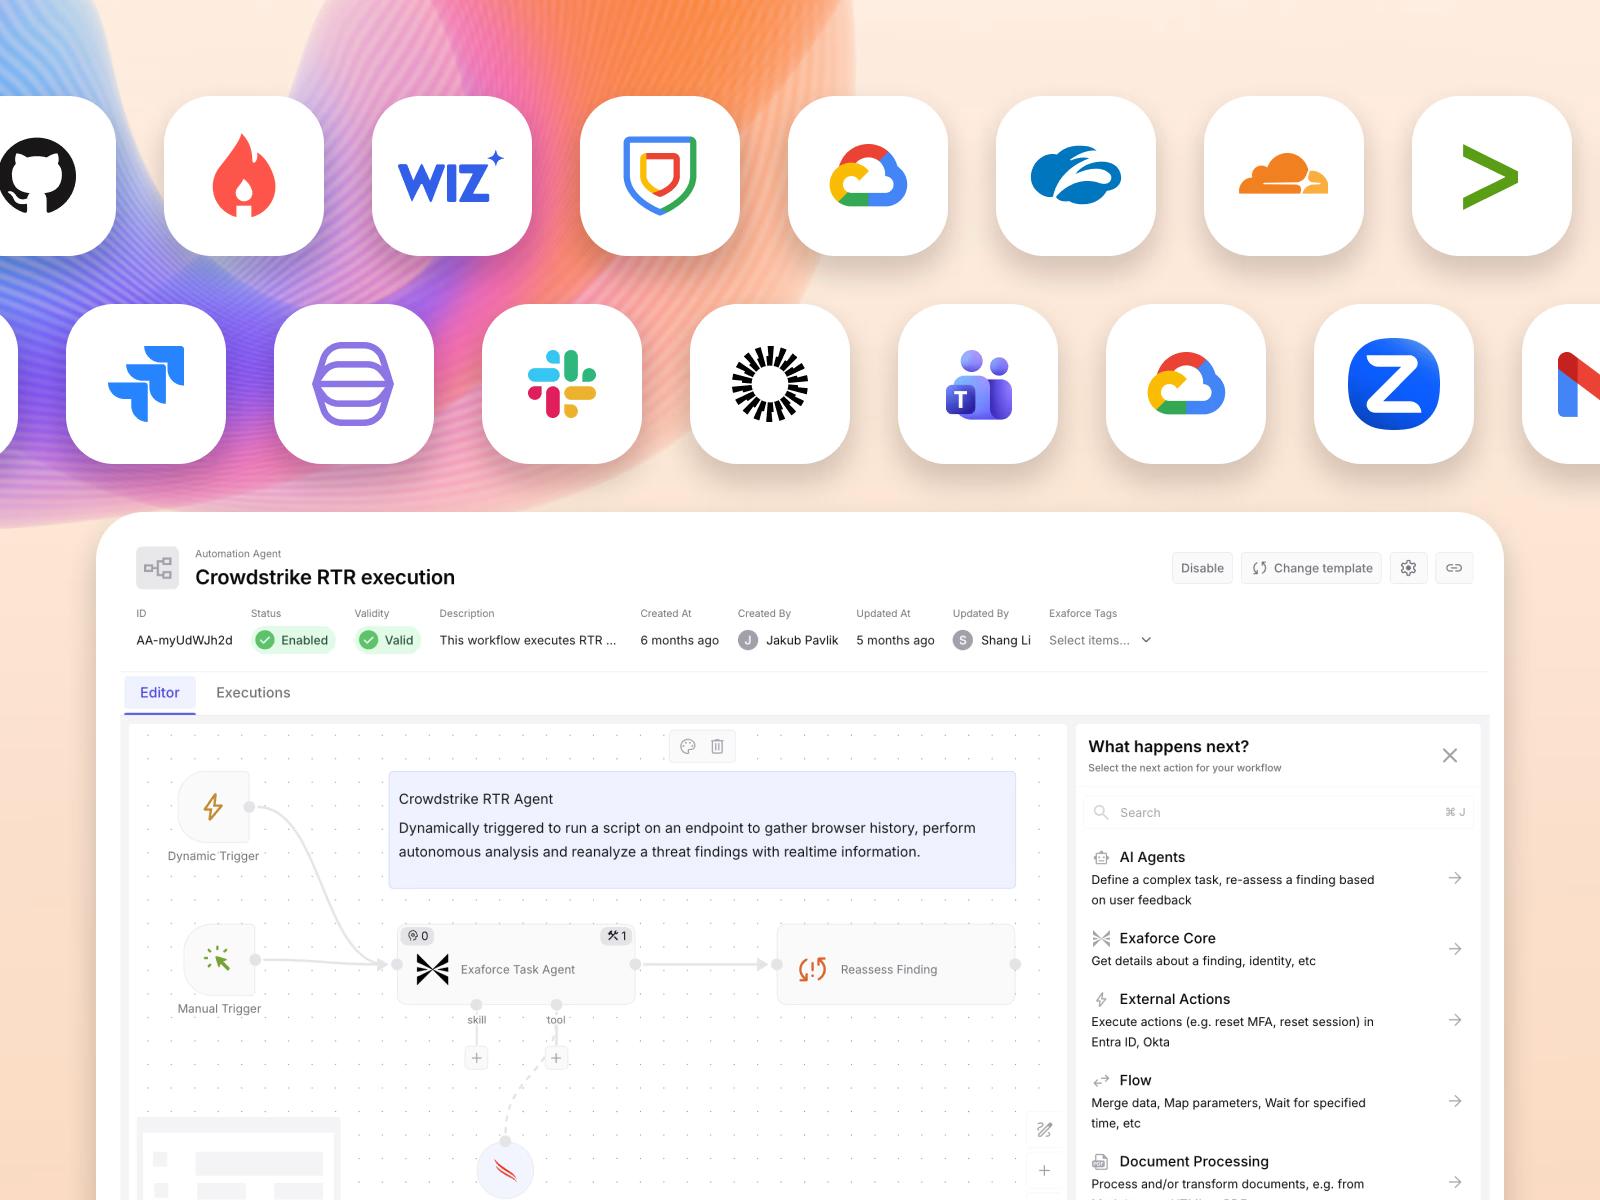
Your AI incident responder. Comes with built-in playbooks, new ones written in plain language, approval gates and an audit trail on every action. Alert-to-response time averages under 30 minutes.
What makes an Exabot different
Most platforms start at the alert. Exaforce starts at the data.
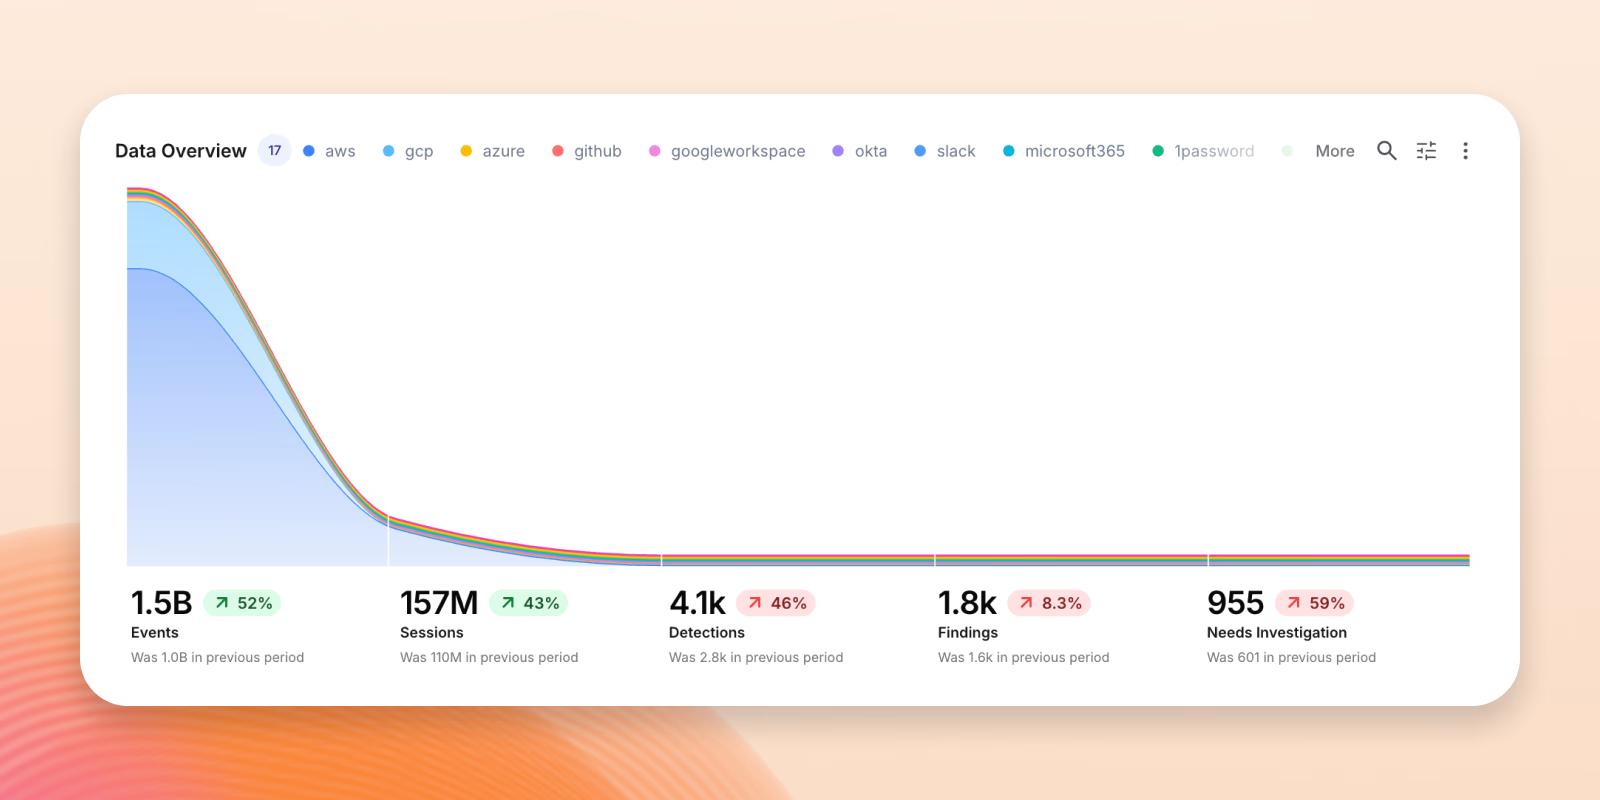
A foundation, not a bolt-on
Bolt-on AI reads raw events and lacks the context to decide. Exabots read a real-time knowledge graph, so hours-long investigations close in minutes.
A foundation, not a bolt-on
Bolt-on AI reads raw events and lacks the context to decide. Exabots read a real-time knowledge graph, so hours-long investigations close in minutes.
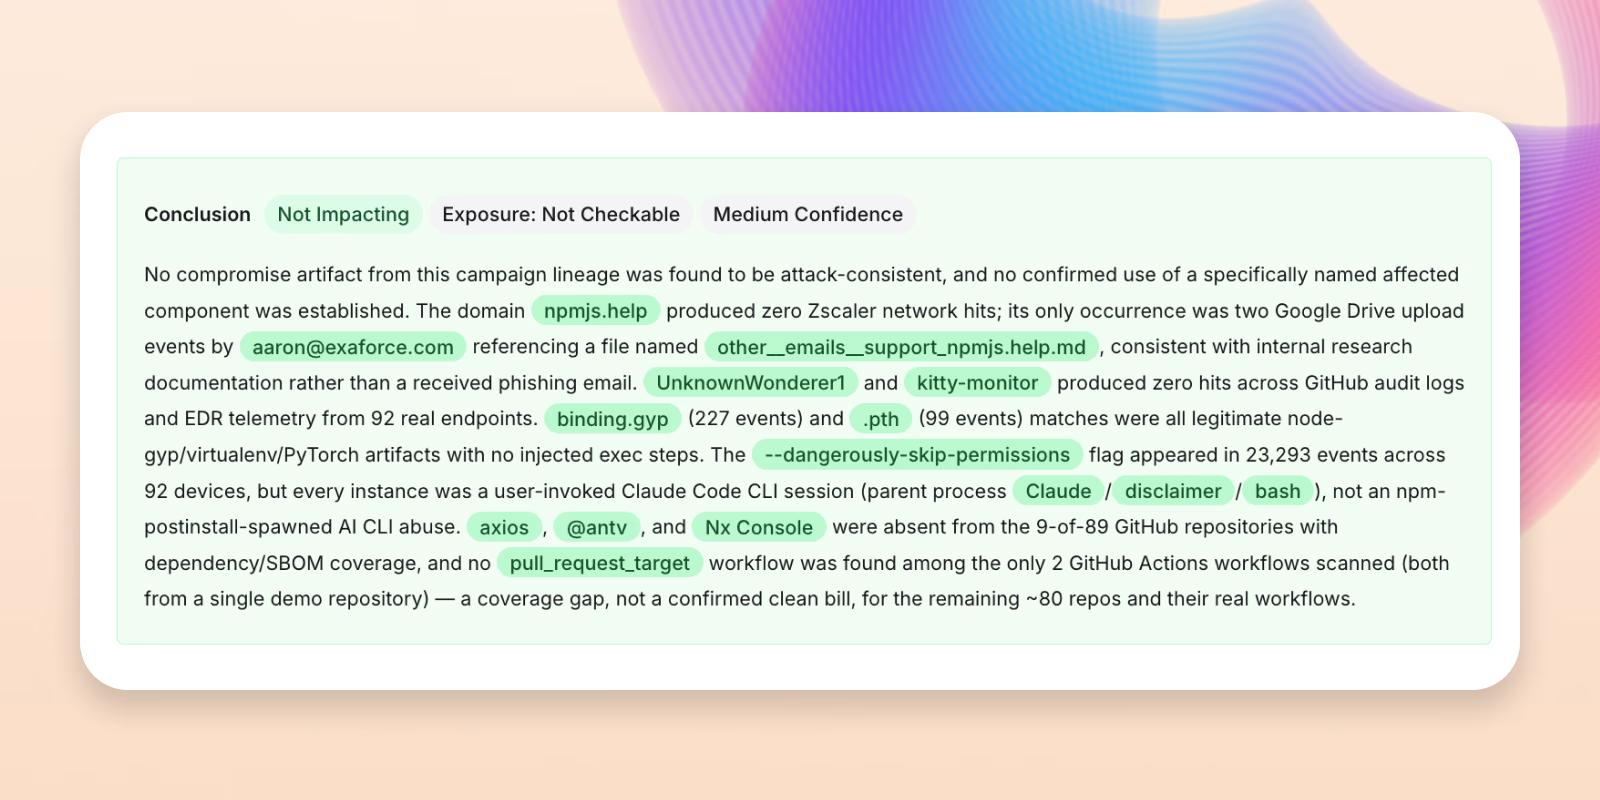
Real-time reasoning
Events, configuration, identity, and resources are correlated first, so an Exabot opens an alert already knowing which identity acted and what changed. Every verdict arrives with the evidence behind it, and your team keeps the judgment calls.
Real-time reasoning
Events, configuration, identity, and resources are correlated first, so an Exabot opens an alert already knowing which identity acted and what changed. Every verdict arrives with the evidence behind it, and your team keeps the judgment calls.
Purpose-built for each role
Each Exabot is built for one role, not adapted from a general-purpose assistant, so it carries the reasoning that role needs. Operate the platform yourself, or have us run it as your MDR.
Purpose-built for each role
Each Exabot is built for one role, not adapted from a general-purpose assistant, so it carries the reasoning that role needs. Operate the platform yourself, or have us run it as your MDR.
Accton
Exaforce has significantly improved our SOC efficacy by augmenting threat detection and response for AWS and Azure with AI. Its auto-triage of third-party alerts and rule-free detection streamlines our response and saves us dozens of hours, letting our team focus on mitigating threats, while their exploration capabilities offer greater visibility into all our Cloud services.
CISO & CIO at Accton