
Blog
Insights that keep you ahead
Explore expert perspectives, practical tips, and the latest trends shaping the cybersecurity landscape.
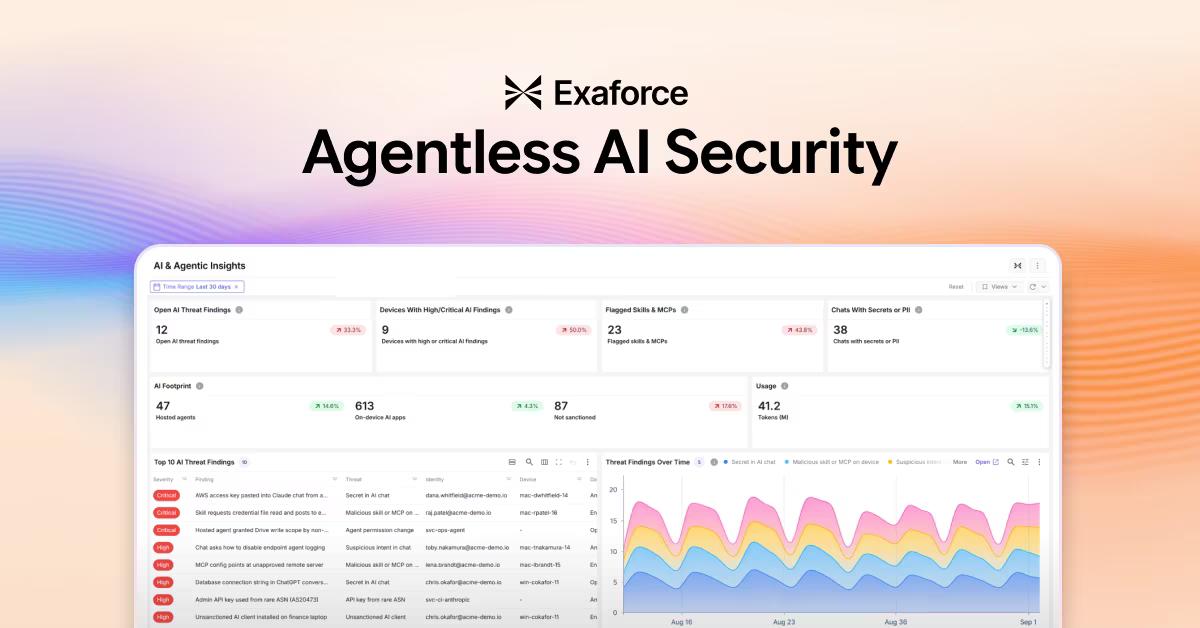
Expanding beyond the SOC: Introducing Exaforce Agentless AI Security
Secure enterprise AI agents and applications from endpoint to cloud by bridging context from the Exaforce Knowledge Graph to identify risks, detect threats, and stop malicious activity or misuse in real time without deploying another security agent.
 Lahav Ezer
Expanding beyond the SOC: Introducing Exaforce Agentless AI Security
Why SIEMs Fall Short for Modern Threat Detection
No Off-the-Shelf Kit Required: An overview of a custom AiTM phishing campaign found in the wild and the mechanisms behind it
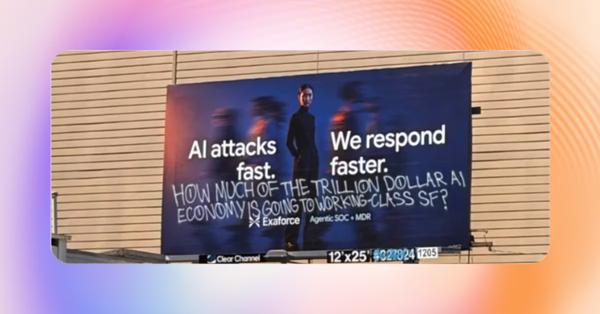
San Francisco tattooed Exaforce’s first billboards campaign. And honestly, we get it.
Caught in the Middle: Responding to an AiTM Credential Heist
Introducing InfOSAStealer: ClickFix Delivery, Fake System Dialogs, and the Quiet Trojanization of Hardware Wallet Software
Introducing “ExaGo”: Your SOC Now Goes Anywhere You Go
You don’t see me, therefore I am: Taking a look at abusing GitHub’s first party sessions for initial access
Learning from the Exaforce frontline: Detecting GitHub OAuth Token Compromise
The Agentic SOC, Grounded in the Network
The SIEM Possible Challenge: Moving From Events to Answers in a Modern SOC
Claude meets the SOC: Removing the AI blind spot
AWS validated us for AI and Security. Here is what that means.
What the 2026 Latio Security Operations Market Report Gets Right About the AI SOC
Defending at the speed of AI: Announcing our $125M Series B
Exaforce and Wiz: Connecting cloud security findings to SOC response
Vibe Hunting: A New Model for Threat Hunting Beyond SIEM Queries
The Exabots are on strike (this is fine)
There’s a bot in my boot! Finding if hackerbot-claw tried tampered with your workflows
What can this compromised user actually do? Why effective permissions are a cornerstone of accurate threat analysis
Rethinking MSSP repatriation: AI SOCs, in-house builds, and the middle ground
The Phishing Matryoshka: Unpacking a BEC to AiTM Nested Attack Chain
The breach already inside: Operationalizing insider risk management
7 predictions for the security landscape in 2026
Exaforce Agentic SOC 2025 year in review
Learning from the Exaforce frontline: When trusted third parties behave like threat actors
The Call Is Coming from Inside the House: 6 Strategies for Insider Risk
Lessons from the hallways at my first AWS re:Invent
Learning from the Exaforce frontline: Detecting and interrupting a sophisticated Google Workspace intrusion with agentic AI security
Feeding the worm a soft cloudy bun: The second coming of Shai-Hulud
How an AI SOC turns Anthropic’s intelligence report into daily defense
Your AI-driven threat hunting is only as good as your data platform and pipeline
The log rings don’t lie: historical enumeration in plain sight
The past, present, and future of security detections
We’re HITRUST certified: strengthening trust across cloud-native SOC automation
GPT needs to be rewired for security
Aggregation redefined: Reducing noise, enhancing context
Exaforce selected to join the 2025 AWS Generative AI Accelerator
Do you feel in control? Analysis of AWS CloudControl API as an attack tool
Exaforce Named a Leader and Outperformer in the 2025 GigaOm Radar for SecOps Automation
How agentic AI simplifies GuardDuty incident response playbook execution
There’s a snake in my package! How attackers are going from code to coin
Ghost in the Script: Impersonating Google App Script projects for stealthy persistence
Learning from the Exaforce frontline: How Exaforce detected an account takeover attack in a customer’s environment, leveraging our multi-model AI
s1ngularity supply chain attack: What happened & how Exaforce protected customers
Meet Exaforce: The full-lifecycle AI SOC platform
Introducing Exaforce MDR: A Managed SOC That Runs on AI
Building trust at Exaforce: Our journey through security and compliance
Fixing the broken alert triage process with more signal and less noise
Evaluate your AI SOC initiative
One LLM does not an AI SOC make
Detections done right: Threat detections require more than just rules and anomaly detection
The KiranaPro breach: A wake-up call for cloud threat monitoring
3 points missing from agentic AI conversations at RSAC
5 reasons why security investigations are broken - and how Exaforce fixes them
Bridging the Cloud Security Gap: Real-World Use Cases for Threat Monitoring
Reimagining the SOC: Humans + AI bots = Better, faster, cheaper security & operations
Safeguarding against Github Actions(tj-actions/changed-files) compromise
Npm provenance: bridging the missing security layer in JavaScript libraries
Exaforce’s response to the LottieFiles npm package compromise
No matching posts.