
Exaforce + CrowdStrike
Get more from every Falcon detection
Build on your CrowdStrike Falcon investment with AI agents that bring evidence together, reduce manual investigation, and help your team act with confidence. Exaforce connects Falcon detections with your wider environment, with analysts in control.
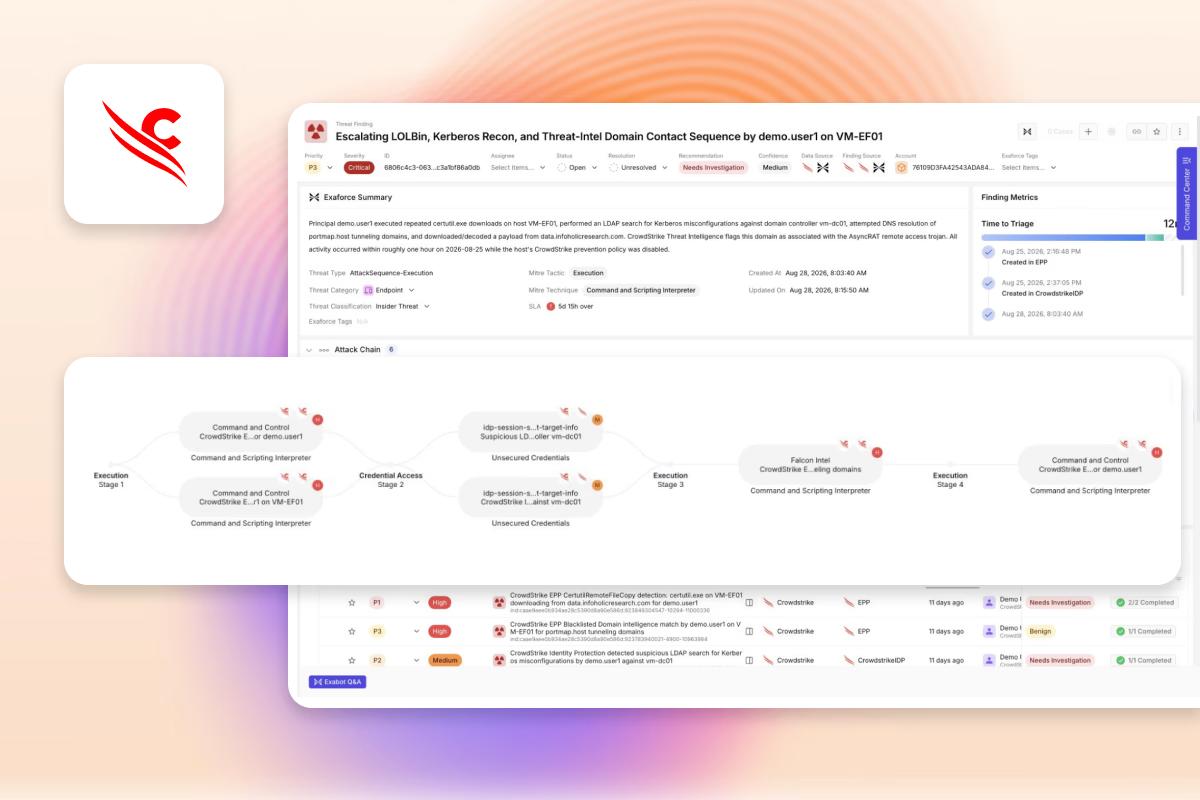
Better together
Stronger investigations with Exaforce and CrowdStrike
CrowdStrike Falcon brings detections, threat intelligence, and response capabilities to your security operations. Exaforce builds on that foundation by connecting Falcon evidence with activity from your other identity, cloud, SaaS, and security tools.
Exaforce’s AI agents, called Exabots, help your team decide what needs attention, understand the scope of an incident, and carry the investigation into an approved response. Analysts can inspect the evidence, question the assessment, and choose the next step.
Less manual triage
Assess Falcon detections with relevant context and an explained recommendation, so analysts can focus on the findings that need attention.
Faster incident scoping
Follow related activity across users, devices, and applications to understand what happened and what may be affected.
Response under your control
Coordinate supported actions through Falcon and connected tools, with permissions and approvals defined by your team.
Function Health
AI-driven analysis is essential for modern security operations, and Exaforce demonstrates how AI can act as a true investigation partner. The company's platform enables our team to operate with the depth and context that traditionally requires a full SOC and significant manual effort, helping us to scale our security efforts to meet our growing needs.
SVP, Security & IT at Function Health
From detection to action
Follow the attack chain across your environment
Start with a Falcon detection, connect the surrounding activity, and use the evidence to decide what happens next.
01 / Triage
Assess the detection
Falcon flags a suspicious script. Exabot Triage brings device, process, and user context into the assessment, with a recommendation and evidence for the analyst.
02 / Scope
Connect the evidence
Follow the same account across tools. An unfamiliar sign-in and unusual downloads add context. Exabot Investigate helps the analyst assess the connections and scope affected users, systems, and data.
03 / Respond
Act with control
Coordinate an approved response. If a threat is confirmed, a configured workflow can isolate the endpoint through Falcon and revoke sessions through the connected identity provider, then record returned results.

Natural language investigation
Work the investigation in the words you would use with a colleague, and read the evidence behind every answer.
Start with a question
“What else did this user access after the suspicious execution?”
Trace it to the evidence
Ask follow-up questions in natural language and follow the answers back to the evidence.
Describe the response
Describe a response workflow in natural language, then review its steps and approval conditions before enabling it.
Demo video
See the integration in action
Follow a Falcon detection through triage, related evidence, and recommended next steps.
Falcon integrations
Connect the Falcon capabilities you already use
Bring the Falcon capabilities you use into a shared investigation. Available connections and actions depend on your licences, enabled integrations, and approved access.

Endpoint
Falcon Insight XDR
Investigate endpoint detections with device and process context, then connect the evidence to activity elsewhere.
Connection and access details
With the required permissions and configured workflows, Exaforce can contain devices, update Falcon alerts, and execute approved actions through Falcon Real Time Response.

Identity
Falcon Next-Gen Identity Security
Connect identity detections to the relevant user, endpoint, and sign-in history to assess account misuse.
Connection and access details
Exaforce adds evidence from your connected identity provider to help scope affected access. Identity response, including session revocation, runs through that provider and requires the appropriate permissions.

SaaS
Falcon Shield
Investigate SaaS-security detections alongside application and identity activity to understand which account is involved and what changed.
Connection and access details
Additional activity comes from the relevant connected SaaS application and identity provider. Available evidence depends on the integrations and access configured in your environment.

SIEM
Falcon Next-Gen SIEM
Search relevant event data on demand to add evidence to an investigation.
Connection and access details
This connection is optional where Falcon Next-Gen SIEM is deployed and authorised. It is not required for the other Falcon integrations.

Threat intelligence
Falcon Adversary Intelligence
Enrich findings with indicator, adversary, malware, and report context to reduce manual threat-intelligence research.
Connection and access details
Requires the relevant Falcon Adversary Intelligence licence and approved access.
Compliance
Commitment to data protection
Exaforce is audited and certified by industry-leading third party standards.
- SOC 2 Type 2Compliant
- SOC 2 Type 1Compliant
- ISO 27001Certified
- PCI DSSCompliant
- HIPAACompliant
- GDPRCompliant
- USDPCompliant
- HITRUSTCertified
Solution brief
Go deeper on the Falcon integration
Placeholder — replace with the approved solution brief summary. The download is disabled until the final PDF URL is supplied.
Download the solution brief (PDF)Resources
More on Exaforce and CrowdStrike
Fixing the broken alert triage process with more signal and less noise
A look at how AI is changing the SOC triage process from automated false positive classification to clearer handoffs and deeper context for Tier 2 and 3 analysts.
Introducing InfOSAStealer: ClickFix delivery, fake system dialogs, and the quiet trojanization of hardware wallet software
This article goes through the analysis of an interesting attack Clickfix attack starting from a shared LLM chat and ending with the malware’s potential financial impact through wallet trojanization.
The past, present, and future of security detections
Modern detection goes beyond static rules by understanding the signals that reveal intent, context, and emerging threats.