Microsoft Sentinel is Microsoft's cloud-native SIEM and SOAR, now delivered through the Microsoft Defender portal, with a data lake tier for lower-cost retention and Security Copilot able to work on its data. Teams look for a Microsoft Sentinel alternative when analytics-tier ingest pricing forces choices about which logs to keep, when KQL detection rules need more tuning than the team can give them and analysts still investigate most alerts by hand, or when a large non-Microsoft estate makes the integration less seamless than it is in a Microsoft-only environment. This guide covers what Sentinel does, when teams look elsewhere, how to compare, and five options that either replace Sentinel or take the work off the top of it. Exaforce publishes this page and is one of the five; it ingests Sentinel, Defender, Entra ID and Microsoft 365 telemetry as sources.
What Microsoft Sentinel does
Sentinel collects logs from Microsoft and third-party sources, runs KQL-based analytics rules, and automates response through playbooks. It is moving fully into the Defender portal: Microsoft has said Sentinel will no longer be supported in the Azure portal after March 31, 2027. Pricing is per GB analyzed, with commitment tiers and a lower-cost data lake tier for long-term retention. Security Copilot provides generative AI assistance on Sentinel data. (As published by Microsoft, Nov 2026.)
Why teams look for a Microsoft Sentinel alternative
- Ingest cost shapes coverage. Per-GB pricing on the analytics tier means every new source is a budget decision. Teams that send cloud and SaaS logs elsewhere, or not at all, to control the bill have a detection gap by another name.
- KQL rules need an owner. Detections written in KQL need tuning as the environment changes, and analytics rules raise alerts for analysts to investigate; the investigation itself is still manual unless something sits on top.
- Non-Microsoft estates fit less neatly. AWS, Google Cloud, Okta and a large SaaS footprint are supported through connectors, but the native experience is Microsoft-first.
- The portal move is a natural review point. A change of console is when teams ask whether the SIEM itself is still the right shape.
How to compare the options
- Replace or sit on top: some options replace Sentinel; others keep it and automate the work above it.
- Pricing unit: per GB, per module, per platform. Ask what you would collect if ingest were not metered.
- Detection ownership: rules the team writes and tunes, or detections that run on a model of the environment.
- Investigation completion: how many alerts arrive with the investigation done.
- Non-Microsoft coverage: identity, cloud and SaaS from every vendor treated the same way at ingest.
Five Microsoft Sentinel alternatives at a glance
Exaforce
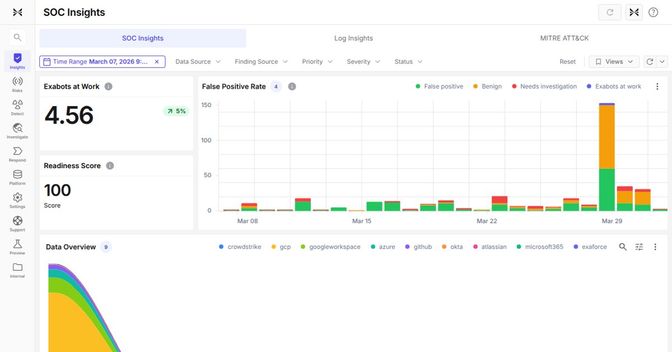
Exaforce is an agentic SOC platform with a data platform of its own. It ingests logs, identity data, configuration and code from 130+ sources, including Sentinel, Defender, Entra ID and Microsoft 365 as well as AWS, Google Cloud, Okta and the SaaS estate, and resolves each event at ingest against a model of identities, resources and their relationships; its own detections run on that model. The Exabots, its AI agents, detect, triage, investigate and respond on the same context, with the reasoning shown on every verdict and the actions you choose gated for approval. With ExaU, teams build their own Exabots for the work specific to them. Customers report 90% fewer false positives and a 95% reduction in mean time to investigate, with an average of under 30 minutes from alert to response. Teams run it themselves or have Exaforce MDR run it. Teams either replace the SIEM outright or run Exaforce alongside Sentinel during a transition, with Sentinel as one source among many. See the Microsoft Sentinel integration and SIEM augmentation for the alongside option.
Palo Alto Networks Cortex XSIAM
Cortex XSIAM combines SIEM, XDR, automation and AI analytics on one data layer and is strongest where Palo Alto Networks supplies the telemetry. See Palo Alto Networks alternatives.
CrowdStrike Falcon Next-Gen SIEM
Falcon Next-Gen SIEM extends the Falcon endpoint platform into log management and detection with Charlotte AI as the analyst, and is strongest where Falcon is on every device. See Microsoft Sentinel vs CrowdStrike.
Google Security Operations
Google Security Operations is a cloud-native SIEM and SOAR built for very high log volumes and long retention, with Google's threat intelligence alongside. The fit is a team whose first problem is the volume and the retention term rather than the investigation.
Torq
Torq keeps Sentinel in place and adds Auto Triage, the Socrates remediation agent and case management on a hyperautomation engine. The fit is a team that wants to keep the SIEM and automate the response layer with workflows it builds. See Torq alternatives.
Choosing the right Sentinel alternative
- Microsoft-centric with manageable ingest: staying with Sentinel and adding AI on top is a reasonable answer; measure the analyst hours first.
- Ingest cost is the problem: compare pricing units before features, and include what you are not collecting today.
- Analyst workload is the problem: compare how much investigation each platform completes on its own.
- Both, in a cloud-first estate: a platform with its own data layer and its own investigation, run alongside Sentinel first if the migration needs staging.
Pilot the shortlist with your own data and measure two things: the bill, and the number of alerts that still need a person.
Frequently asked questions
What is the best Microsoft Sentinel alternative?
It depends on the problem. For ingest cost, compare pricing units; for analyst workload, compare how much investigation the platform completes; for a mixed or AWS-first estate, a platform that treats every source the same way at ingest.
Is Sentinel being retired?
No. Sentinel is moving fully into the Microsoft Defender portal, and Microsoft has said it will not be supported in the Azure portal after March 31, 2027. The product continues; the console changes.
Can Exaforce run alongside Microsoft Sentinel?
Yes. Exaforce ingests Sentinel and the rest of the Microsoft estate as sources and runs its own detections and investigation across them, which is how many teams stage a SIEM transition. See SIEM migration.
Which alternative keeps Sentinel and adds AI on top?
Torq, for workflow-built triage and response; Security Copilot, for assistance inside the console. For investigation completed on a model of the environment, Exaforce alongside Sentinel.