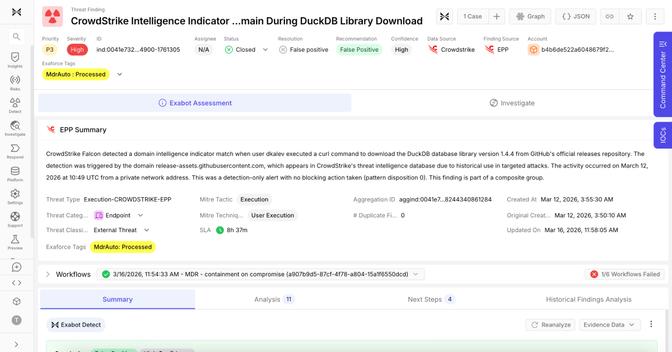
This page is about the SOC layer, not the endpoint. CrowdStrike's Falcon platform is the endpoint agent many security teams standardize on, and CrowdStrike now sells the layers above it too: Falcon Next-Gen SIEM for log management and detection, Charlotte AI as an agentic analyst, and Charlotte Agentic SOAR for orchestration. Teams that keep Falcon on every device still choose where the SIEM and the AI SOC layer live, and they look at alternatives when most of their investigations now start in identity providers, cloud control planes and SaaS rather than on a device, when they run a mixed-vendor estate, or when they want one platform for the data and the investigation. This guide covers the SOC layer CrowdStrike offers, when teams look elsewhere for it, how to compare, and five options to test. Exaforce publishes this page and is one of the five; it ingests Falcon telemetry as a source.
What CrowdStrike offers above the endpoint
Falcon Next-Gen SIEM extends the Falcon platform into log management and detection; Charlotte AI is CrowdStrike's agentic security analyst built on the platform; Charlotte Agentic SOAR adds orchestration; and Charlotte AI AgentWorks is a no-code environment for building agents. The design is one platform anchored on the Falcon agent's telemetry, with third-party data brought in alongside it. Licensing is module-based. (Product names as published by CrowdStrike, Nov 2026.)
Why teams look for an alternative at the SOC layer
- Your incidents no longer start on a device. An AI layer anchored on endpoint telemetry has the most context on the endpoint. When the first alert is an OAuth grant, an IAM role or a SaaS admin change, ask how much context the platform has there.
- Your estate is mixed. With more than one EDR, several clouds and a large SaaS footprint, third-party data has to be a first-class citizen, not an add-on to one vendor's telemetry.
- You want to choose each layer separately. Endpoint, SIEM and SOC automation from one vendor is simple to buy and hard to leave. Some teams want the endpoint decision and the SOC decision to stay independent.
- Module pricing is hard to forecast. As sources and modules grow, so does the bill, and the SIEM part is priced differently from the endpoint part.
How to compare the options
- Where the context is strongest: endpoint, or identity, cloud and SaaS. Match it to where your incidents start.
- How third-party data is treated: normalized into one model at ingest, or searched as logs.
- How far the platform goes: detections of its own, or an AI layer over detections other tools produce.
- Pricing unit: per module, per GB, per endpoint, per platform.
- What stays independent: whether you can change the endpoint vendor later without changing the SOC.
Five CrowdStrike alternatives at a glance
Exaforce
Exaforce is an agentic SOC platform with a data platform of its own. It ingests logs, identity data, configuration and code from 130+ sources, including Falcon and the other EDRs, identity providers, cloud control planes and SaaS applications, and resolves each event at ingest against a model of identities, resources and their relationships; its own detections run on that model. The Exabots, its AI agents, detect, triage, investigate and respond on the same context, with the reasoning shown on every verdict and the actions you choose gated for approval. With ExaU, teams build their own Exabots for the work specific to them. Customers report 90% fewer false positives and a 95% reduction in mean time to investigate, with an average of under 30 minutes from alert to response. Teams run it themselves or have Exaforce MDR run it. Falcon stays where it is; Exaforce adds the cloud, SaaS and identity context around each endpoint detection and takes the investigation from there. See the CrowdStrike integration.
Palo Alto Networks Cortex XSIAM
Cortex XSIAM combines SIEM, XDR, automation and AI-driven analytics on one data layer, and delivers the most value where Palo Alto Networks firewalls, endpoints and cloud security already supply the telemetry. The fit is an enterprise standardizing on Palo Alto Networks. See Palo Alto Networks alternatives and CrowdStrike vs Palo Alto Networks.
Microsoft Sentinel with Security Copilot
Sentinel is Microsoft's cloud-native SIEM and SOAR, now delivered through the Defender portal, with Security Copilot able to work on its data and a data lake tier for lower-cost retention. The fit is an organization whose identity, email and productivity data already live in Microsoft. See Microsoft Sentinel alternatives and Microsoft Sentinel vs CrowdStrike.
Torq
Torq positions an AI SOC platform on a hyperautomation engine: Auto Triage, the Socrates remediation agent and case management, orchestrating the tools you have. The fit is a team with automation engineers and bespoke response workflows. See Torq alternatives.
Intezer
Intezer applies memory analysis, reverse engineering and sandboxing to the artifacts behind an alert and returns a verdict with evidence, priced per endpoint. It works on the alerts Falcon and your other tools raise, so it is an investigation layer rather than a SIEM replacement. See Intezer alternatives.
Choosing the right CrowdStrike alternative
- Most incidents start and end on endpoints: the native stack is a strong fit; this page will not change your mind.
- Investigations regularly reach identity and cloud: compare how far each option follows them, and on what model.
- You are standardized on another large vendor: its SOC platform will have the same strengths on its own telemetry.
- You want the endpoint and the SOC decided separately, with one platform for data and investigation: Exaforce, with Falcon as a source.
Run a pilot on a few weeks of real alerts and measure one thing: how many still need an analyst after the platform has worked them.
Frequently asked questions
Is this page about replacing CrowdStrike Falcon on the endpoint?
No. It is about the SIEM and AI SOC layer above the endpoint. Every option here can take Falcon telemetry as a source.
What is the best CrowdStrike alternative for cloud and identity investigations?
A platform whose data model and detections are built for identities, cloud resources and SaaS, with endpoint telemetry as one source among them. On this list, Exaforce; the two large-vendor platforms are strongest on their own telemetry.
Can Exaforce work with CrowdStrike?
Yes. Exaforce ingests Falcon telemetry alongside identity, cloud and SaaS sources and investigates across all of them. See the integration page.
What is the best CrowdStrike Next-Gen SIEM alternative?
If ingest cost drives the decision, compare pricing units first; if analyst workload does, compare how much investigation each platform completes on its own. See SIEM replacement.